
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Deployment Architecture
- :
- Splunk Enpterprise - Indexer Cluster issue
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
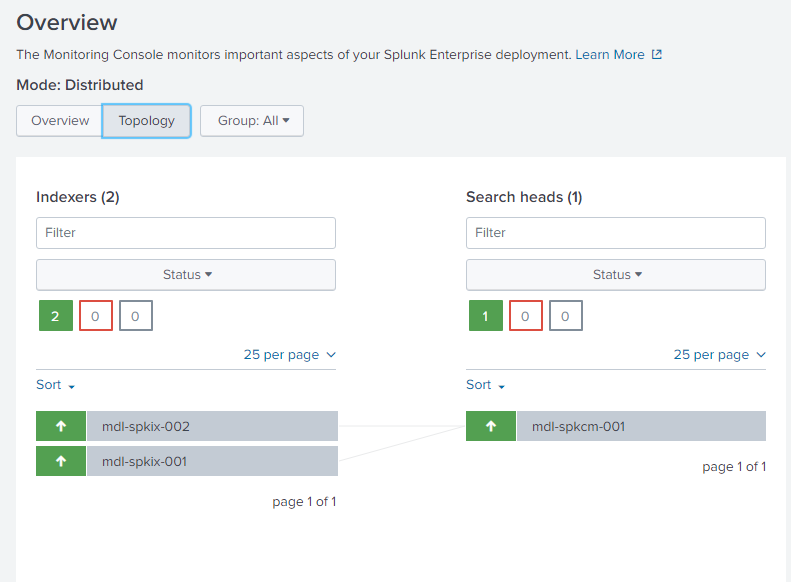
Why I am not able to see Search Heads connection in Cluster Master Monitoring Console - Overview Dashboard (See 1st image)
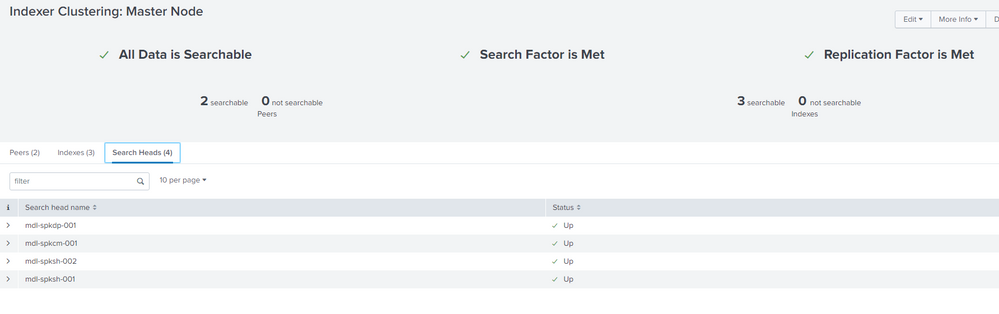
However, I did successful connection to Cluster Master from both Search Heads. (See 2nd image)
I referred below documentation (Integrate the search head cluster with an indexer cluster):
https://docs.splunk.com/Documentation/Splunk/7.2.0/DistSearch/SHCandindexercluster
Background of Architecture:
1 CM,
2 Indexers (Indexer Clustered),
2 Search Heads (Search Head Clustered),
1 Deployer
1 Deployment Server
1 Heavy Forwarder
Splunk Enterprise: 7.2
OS: Centos 7
Splunk License - When you first install a copy of Splunk Enterprise, the installed instance uses a 60 day trial license.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @kishor_pinjarkar_ebay,
at first, did you configured all your Splunk servers (also Deployer and Search Heads) to forward their internal logs to Indexers?
Then, you should see in DMC all the Splunk servers but you have to configure their roles in Monitoring Console Setup [Monitoring Console -- Settings -- Setup].
At https://docs.splunk.com/Documentation/Splunk/8.0.1/DMC/DMCoverview you can find all the infos you need to do this.
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @kishor_pinjarkar_ebay,
at first, did you configured all your Splunk servers (also Deployer and Search Heads) to forward their internal logs to Indexers?
Then, you should see in DMC all the Splunk servers but you have to configure their roles in Monitoring Console Setup [Monitoring Console -- Settings -- Setup].
At https://docs.splunk.com/Documentation/Splunk/8.0.1/DMC/DMCoverview you can find all the infos you need to do this.
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I missed this step - https://docs.splunk.com/Documentation/Splunk/8.0.1/DMC/Addinstancesassearchpeers
Now it's working fine.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Also checked, Cluster Master Monitoring Console - Instances dashboard.
They are not showing up there.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Is it because of different secret key for each - Indexer Cluster and Search Head Cluster?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Yes, forwarded logs from both Search Heads and Deployer.
Yes, I did role configuration earlier.
Still no luck now. Let me read the docs -https://docs.splunk.com/Documentation/Splunk/7.2.0/DMC/DMCoverview




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
Announcing Modern Navigation: A New Era of Splunk User Experience
