
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Dashboards & Visualizations
×
Join the Conversation
Without signing in, you're just watching from the sidelines. Sign in or Register to connect, share, and be part of the Splunk Community.
- Find Answers
- :
- Using Splunk
- :
- Dashboards & Visualizations
- :
- Re: Hide HTML with simple checkbox
Options
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
mclane1
Path Finder
09-28-2021
12:56 AM
Hello
<row>
<panel>
<title>Manage alerts</title>
<input type="checkbox" token="detail_input_token">
<label></label>
<choice value="hide">Hide detail</choice>
<initialValue>hide</initialValue>
</input>
<html>debug detail_input_token:$detail_input_token$</html>
<html rejects="$detail_input_token$">
<body>
<p>
<A HREF="/manager/myapp/data/lookup-table-files?ns=myapp&pwnr=-&search=mySearch&count=100" target="_blank">
Manage <B>lookup mySearch</B> (csv files).
</A>
</p>
</body>
</html>
</panel>
</row>
It works in splunk 6.4.2
We migrate on splunk 8.2 and it doesn't work now.
I do many change without success.
Does somebody have an idea ?
Thanks in advance.
1 Solution
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
mclane1
Path Finder
10-04-2021
07:32 AM
I find solution.
When we have already many inputs you must specify the searchWhenChanged and set to "true"
<row>
<panel>
<title>Manage alerts</title>
<input type="checkbox" token="detail_input_token" searchWhenChanged="true">
<label></label>
<choice value="hide">Hide detail</choice>
<initialValue>hide</initialValue>
</input>
<html>debug detail_input_token:$detail_input_token$</html>
<html rejects="$detail_input_token$">
<body>
<p>
<A HREF="/manager/myapp/data/lookup-table-files?ns=myapp&pwnr=-&search=mySearch&count=100" target="_blank">
Manage <B>lookup mySearch</B> (csv files).
</A>
</p>
</body>
</html>
</panel>
</row>Now it works
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

kamlesh_vaghela

SplunkTrust
10-04-2021
08:09 AM
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
mclane1
Path Finder
10-05-2021
01:32 AM
Is it ok ?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
kamlesh_vaghela
SplunkTrust
10-03-2021
11:21 PM
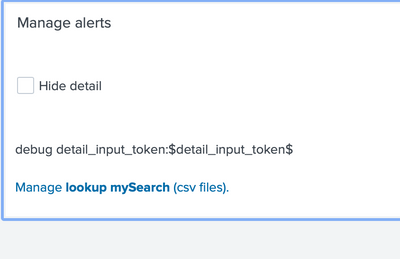
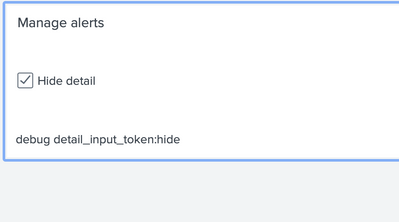
The checkbox behaviour working for me on Splunk Version: 8.2.2.1.
It that anything specific which not working?
Thanks
KV
▄︻̷̿┻̿═━一 😉
If any of my reply helps you to solve the problem Or gain knowledge, an upvote would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
mclane1
Path Finder
10-04-2021
07:32 AM
I find solution.
When we have already many inputs you must specify the searchWhenChanged and set to "true"
<row>
<panel>
<title>Manage alerts</title>
<input type="checkbox" token="detail_input_token" searchWhenChanged="true">
<label></label>
<choice value="hide">Hide detail</choice>
<initialValue>hide</initialValue>
</input>
<html>debug detail_input_token:$detail_input_token$</html>
<html rejects="$detail_input_token$">
<body>
<p>
<A HREF="/manager/myapp/data/lookup-table-files?ns=myapp&pwnr=-&search=mySearch&count=100" target="_blank">
Manage <B>lookup mySearch</B> (csv files).
</A>
</p>
</body>
</html>
</panel>
</row>Now it works


Got questions? Get answers!
Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Meet up IRL or virtually!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Get Updates on the Splunk Community!
Supercharging Windows Security Detection Performance: Introducing Hybrid Field ...
Windows event logs—from Security auditing and Sysmon to PowerShell script blocks—form the operational backbone ...
Enriching Signals with the OTel Lookup Processor
Introduction
Raw telemetry is often incomplete. A log line might record an IP address, but what you really ...
Meet the .conf26 AI Agent Buildathon Winners
At the .conf26 AI Agent Buildathon, Splunk users turned their operational expertise into working AI agents ...
