
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Dashboards & Visualizations
- :
- Re: Display TV guide style UI in dashboard
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

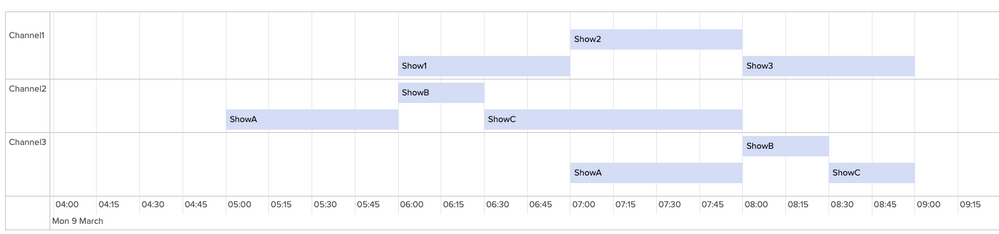
I am new to Splunk and I need to display my data in typical TV guide format.
X axis is list of channels
Y axis is timeline with scroll bar to go left and right of the current time.
Each row of the line is a variable length rectangles that show the program.
What is the best way to achieve this in splunk dashboard?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

1) Install the Event Timeline Viz
https://splunkbase.splunk.com/app/4370/
2) Here is a sample query. After execution, go to Visualisation, and select Event Timeline Viz. You will see the result displayed like a TV guide.
| makeresults
| eval raw = "Channel1%Show1%6:00:00 PM%7:00:00 PM;Channel1%Show2%7:00:00 PM%8:00:00 PM;Channel1%Show3%8:00:00 PM%9:00:00 PM;Channel2%ShowA%5:00:00 PM%6:00:00 PM;Channel2%ShowB%6:00:00 PM%6:30:00 PM;Channel2%ShowC%6:30:00 PM%8:00:00 PM;Channel3%ShowA%7:00:00 PM%8:00:00 PM;Channel3%ShowB%8:00:00 PM%8:30:00 PM;Channel3%ShowC%8:30:00 PM%9:00:00 PM"
| makemv raw delim=";"
| mvexpand raw
| rex field=raw "(?P<Channel>[^\%]+)%(?P<Show>[^\%]+)%(?P<Start_Time>[^\%]+)%(?P<Finish_Time>[^\%]+)"
| eval time_1 = strptime(Start_Time, "%H:%M:%S %p")
| eval time_2 = strptime(Finish_Time, "%H:%M:%S %p")
| eval duration = time_2 - time_1
| eval group = Channel, label = Show, start = time_1, end = time_2, tooltip = Show
| table group, label, start, end, tooltip
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
1) Install the Event Timeline Viz
https://splunkbase.splunk.com/app/4370/
2) Here is a sample query. After execution, go to Visualisation, and select Event Timeline Viz. You will see the result displayed like a TV guide.
| makeresults
| eval raw = "Channel1%Show1%6:00:00 PM%7:00:00 PM;Channel1%Show2%7:00:00 PM%8:00:00 PM;Channel1%Show3%8:00:00 PM%9:00:00 PM;Channel2%ShowA%5:00:00 PM%6:00:00 PM;Channel2%ShowB%6:00:00 PM%6:30:00 PM;Channel2%ShowC%6:30:00 PM%8:00:00 PM;Channel3%ShowA%7:00:00 PM%8:00:00 PM;Channel3%ShowB%8:00:00 PM%8:30:00 PM;Channel3%ShowC%8:30:00 PM%9:00:00 PM"
| makemv raw delim=";"
| mvexpand raw
| rex field=raw "(?P<Channel>[^\%]+)%(?P<Show>[^\%]+)%(?P<Start_Time>[^\%]+)%(?P<Finish_Time>[^\%]+)"
| eval time_1 = strptime(Start_Time, "%H:%M:%S %p")
| eval time_2 = strptime(Finish_Time, "%H:%M:%S %p")
| eval duration = time_2 - time_1
| eval group = Channel, label = Show, start = time_1, end = time_2, tooltip = Show
| table group, label, start, end, tooltip
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

@prashantku you can try out Timeline Custom Visualization built by Splunk.
| makeresults | eval message= "Happy Splunking!!!"
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


timechart will give you a timeline on the x axis and data on the y axis. The transpose command will swap those. Perhaps that will get you going in the right direction. If not, please elaborate on what you want and include some sample data.
If this reply helps you, Karma would be appreciated.



Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
