
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Other Using Splunk
- :
- Alerting
- :
- How to include time field in email message body?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi All,
I'm setting an alert and sending email notification to my inbox.
I have a field called Time and basically it calculates the duration. Example: "25 minutes ago"
Hence , when I include the field in the message , like below:
$result.Time$
I get message in my inbox in seconds.
Example:
Host abcd CPU usage reached 97% 1680502445 . Please investigate.
So if you look here , the 1680502445 is the time duration in seconds.
It suppose to pick the summarized time as per the column result.
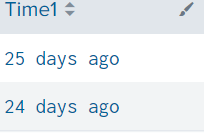
Please help how can I get the same output like what I have gathered in the Time1 column.
Thanks
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @Murali,
could you share your search?
probably the issue is in the Time formatiing, e.g. you could add at the end of your search:
| eval Time=tostring(Time, "duration")Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @Murali,
could you share your search?
probably the issue is in the Time formatiing, e.g. you could add at the end of your search:
| eval Time=tostring(Time, "duration")Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @Murali,
good for you, see next time!
Ciao and happy splunking
Giuseppe
P.S.: Karma Points are appreciated 😉


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
