
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: rex a string from text
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

How do I extract the cities from this text?
\"timezone\"😕"America/Sao_Paulo\",\"max_counter\":2,\"timezone\":\"America/Brasilia\",\"max_counter\":2...
I tried to compute the following query: ... | rex field=city "city: (?<America>)" | top limit=20 city
Thanks!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

this works in regex101
| rex "timezone\\(.*?)\/(?<city>[^\\]+)"
- working in Splunk
| rex "timezone\\\(.*?)\/(?<city>[^\\\]+)"
upvote if this works
If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

If your log is JSON, please _raw text. not your modified samples.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
hey guys, here the real sample:
{\"dialog_node\"😕"node_1_1512565351738\",\"title\"😕"TAG_TEL_2.1.01_xingamentos - Ofensas - Nós de transferência\",\"conditions\"😕"intents[0].confidence > 0.7\"}],\"log_messages\":[]},\"context\":{\"CONTENT_OMITTEDa\":{\"CONTENT_OMITTEDt\"😕"NextChatV1\"},\"conversation_id\"😕"d4d7e1fa-7ecc-4eed-b496-f6a24d0c52fa\",\"system\":{\"initialized\":true,\"dialog_stack\":[{\"dialog_node\"😕"node_1_1512565351738\"}],\"dialog_turn_counter\":18,\"dialog_request_counter\":18,\"_node_output_map\":{\"Welcome\":[0],\"node_4_1545219778942\":[0,0],\"node_6_1506019673483\":[0],\"node_10_1586976201933\":{\"0\":[0]},\"response_89_1586976254180\":{\"0\":[0]},\"node_85_1586976254180\":{\"0\":[0]},\"node_1_1507049882219\":[0],\"response_202_1586977011758\":[0],\"response_192_1586977011758\":{\"0\":[0]},\"response_186_1586977011758\":{\"0\":[0]},\"node_182_1586977011758\":{\"0\":[0]},\"node_1_1560349134258\":[0],\"node_1_1516808150030\":[0,2,1,0],\"node_1_1512565351738\":[0]},\"branch_exited\":true,\"branch_exited_reason\"😕"fallback\"},\"algar\":true,\"counter\":1,\"holidays\"😕"[\\\"11/06/20\\\"]\",\"timezone\"😕"America/Sao_Paulo\",\"max_counter\":2,\"lastTopicname\"😕"\",\"threshold_counter\":1,\"transfer_agent_counter\":1,\"teste_oferta_credito_inicio\":false,\"jornada_strut\"😕"next0_geral_-_-_ofensas\"}}","headers":"{content-length=[2036], content-type=[application/json;charset=UTF-8], date=[Mon, 03 Aug 2020 13:48:38 GMT], server=[Apache-Coyote/1.1], x-server_address=[::ffff:10.215.42.116]}","params":null,"status":200,"processingTime":531}
it is one of many, each one is a log containing that info... I am interested in extract the geolocation of them...
Thanks for the help!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
this works in regex101
| rex "timezone\\(.*?)\/(?<city>[^\\]+)"
- working in Splunk
| rex "timezone\\\(.*?)\/(?<city>[^\\\]+)"
upvote if this works
If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

This should work
| rex max_match=0 "\/(?<city>\w+)"
| mvexpand cityIf this reply helps you, Karma would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Did not work, I want to create an extra coulum "city" from the sample text containig: Sao_Paulo and Brasilia
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
It works on my test system.
| makeresults | eval _raw="\"timezone\":\"America/Sao_Paulo\",\"max_counter\":2,\"timezone\":\"America/Brasilia\",\"max_counter\":2..."
| rex max_match=0 "\/(?<city>\w+)"
| mvexpand city
| top limit=20 city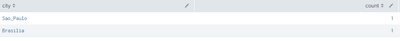
If this reply helps you, Karma would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How it will be writen using the "America" string before? I really need to use it as I put in the example, sorry for dont say that before.
ps: It is beacuse the real text is huge and then matching with /\ will not works, have to be with the "America" word before it.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I didn't assume all of the cities are in the Americas when I made the example. To fix it, just put "America" in the regular expression.
| makeresults | eval _raw="\"timezone\":\"America/Sao_Paulo\",\"max_counter\":2,\"timezone\":\"America/Brasilia\",\"max_counter\":2..."
| rex max_match=0 "America\/(?<city>\w+)"
| mvexpand city
| top limit=20 cityIf this reply helps you, Karma would be appreciated.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Accelerate Splunk App Development with AI
Splunk Agent Observability: Measuring AI Value with Splunk Tokenomics on AWS
Enterprise Security Watch Party: What’s New in 8.8 - Recap
