
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Search empties during run
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi all.
I have a search that searches a large amount of events.
Its run on fast mode, on the statistics page.
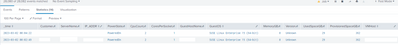
When i start the search it slow starts populating the fields, but then at one point it just empties all the results and says "No results found", even thought they were there at the beginning of the search running...
Any ideas what could be the issue here? Never had anything like this before on other large searches though
Some setting in limits.conf or something?
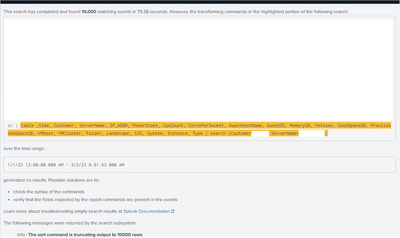
All i get is this, which makes no sense since data is there at the start of the search
In the beginning it shows data:
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Since you have blanked out most of your search, it is difficult to say, if I were to guess, I would say that the sort truncated your results such that there were no longer any results which matched your search criteria. Try using
| sort 0- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
So this was the solution. Can you explain to me why the sorting would just hide ALL the results, instead of showing the last 10.000 like it says it does?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
It is not the sorting which hides the results per se. The sorting (without the zero) has been truncated (according to your screenshot) so not all the events are present. The part of the search that you did leave visible shows a search based on the values of certain fields. My guess is that within the truncated set of events, there were no matches for this search.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
[Puzzles] Solve, Learn, Repeat: Classic British Rock Bands
New to the Community? Join Us for an Exclusive Post .conf26 Welcome Session (Plus a ...
Accelerate Splunk App Development with AI
