
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- URL Decoding- How to resolve error?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
URL Decoding- How to resolve error?

i tried all splunk answers and doesn't seems like working for me.
i have this
search | rex mode=sed field=message.UA "s/%2f///g" | table message.UA
sample message.UA
Mozilla%2f5.0%20(X11%3b%20Linux%20x86_64)%20AppleWebKit%2f537.36%20(KHTML,%20like%20Gecko)%20Chrome%2f70.0.3538.77%20Safari%2f537.36
i got this error after ran the search above.
Error in 'rex' command: Failed to initialize sed. Invalid option string: /g
I tried urldecode function, doesn't work, and also tried almost every solutions from splunk answer, i just could not decode the encoded UA field. please help.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


How about eval's urldecode?
| eval decoded=urldecode(yourEncodedField)
or
| eval decoded=urldecode("yourEncodedString")
https://docs.splunk.com/Documentation/SCS/current/SearchReference/TextFunctions#urldecode.28.26lt.3B...
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

I used your example, and it worked for me. Did you try this way?
| makeresults
| eval ua = "Mozilla%2f5.0%20(X11%3b%20Linux%20x86_64)%20AppleWebKit%2f537.36%20(KHTML,%20like%20Gecko)%20Chrome%2f70.0.3538.77%20Safari%2f537.36"
| eval uadecoded = urldecode(ua)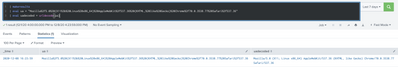
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
@yonphang ,
Try
|rex mode=sed field=url "s/%2f/\//g"
What goes around comes around. If it helps, hit it with Karma 🙂
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
yes that was intentional, i want to find %2f and replace into /
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Ok updated the answer
What goes around comes around. If it helps, hit it with Karma 🙂


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Meet Splunk Observability Studio: AI-Assisted OpenTelemetry Instrumentation Without ...
Federated Search for Cisco Security and Analytics Logging (SAL) is now GA on Splunk ...
Your Path to AgenticOps: AI Experiences for Every Splunk Practitioner
