
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- I need to split the requestPath eliminating the da...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi,
Need one Help. I have the below mentioned requestPath where I am able to capture the whole path..But can't take a count if there is different Div ID and Account No. I just to extract only
"/ecp/stream/v1/purchase/" and make a count of it. so that I can get the different response status
"requestPath":"/ecp/stream/v1/purchase/NTX.8160/8260180902213447","responseStatus":204,"responseSize":0,"responseContent":"","responseTime":27} Show syntax highlighted
rex field=_raw "requestPath":"(?<reqPath>[^?|^\s|^"]+)"
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Try this regex.
... | rex "requestPath":"(?<reqPath>(?:\/[^\/]+){4})"If this reply helps you, Karma would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Try this regex.
... | rex "requestPath":"(?<reqPath>(?:\/[^\/]+){4})"If this reply helps you, Karma would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
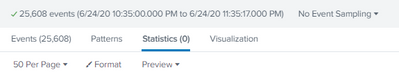
Thanks Rich..I tried the option you gave me. but it's didn't display the request Path nor trimmed it.
My Search "requestPath":"/ecp/stream/v1/purchase*" | rex "requestPath":"(?<reqPath>(?:\/[^\/]+){4})" | stats count by reqPath.
I can see the events but it's not extracting
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi @vijaysubramania
The answer provided by @richgalloway is mostly correct but you'll need to backslash escape the double quotes. Here's a run anywhere example of what I mean.
| makeresults | eval _raw="requestPath\":\"/ecp/stream/v1/purchase/NTX.8160/8260180902213447"
| rex  "requestPath\":\"(?<reqPath>(?:\/[^\/]+){4})"
| stats count by reqPath
Hope this helps.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Got it..Thank you very much Rich and Yeahnah 🙂


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
Announcing Modern Navigation: A New Era of Splunk User Experience
