
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Help with searching command
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

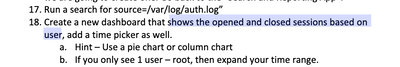
Hi Everyone! I'm having a stuff time trying to figure out a search command for this lab assignment. So I inputted in the search bar, (source=/var/log/auth.log session | top user) and I got the users and a count but not sure if thats the session count. I've tried other ones but don't seem to get the results I need. I need a search command that'll show the opened and closed sessions based on each user so I could create a pie chart showing that data. I'm currently a student in cybersecurity and I'm new to Splunk. Would appreciate the help. Thank you! 🙂
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

The keywords you can use from auth.log for session open is "session opened" and session close is "session closed"
open sessions based on user:
Option: 1 - The below query will give all users and their open sessions count and count will be sorted in descending order. you will see top count first
index=<foo> source=<sourceyoumentionedabove> "session opened" | stats count by user | sort - countOption:2 - The below query will give you same but top by default limit number of rows to 10. To get unlimited users then you should specify top 0 user ( 0 is no limit). top 20 user ( top 20 users).
index=<foo> source=<sourceyoumentionedabove> "session opened" | top 0 userYou can do same for session closed by just replacing "session opened" with "session closed" in above queries.
If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
The keywords you can use from auth.log for session open is "session opened" and session close is "session closed"
open sessions based on user:
Option: 1 - The below query will give all users and their open sessions count and count will be sorted in descending order. you will see top count first
index=<foo> source=<sourceyoumentionedabove> "session opened" | stats count by user | sort - countOption:2 - The below query will give you same but top by default limit number of rows to 10. To get unlimited users then you should specify top 0 user ( 0 is no limit). top 20 user ( top 20 users).
index=<foo> source=<sourceyoumentionedabove> "session opened" | top 0 userYou can do same for session closed by just replacing "session opened" with "session closed" in above queries.
If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thank you very much!!

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
How to Break a Kubernetes Pod on Purpose and Let the AI Troubleshooting Agent Find ...
Splunk Add-on for Microsoft Windows 11.0.3: Parse Once, Search Faster
What's New in Splunk Enterprise Security 8.8 and Beyond
