
Join the Conversation
- Find Answers
- :
- Splunk Products
- :
- Splunk Enterprise Security
- :
- OpenLDAP add-on fields extraction
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
OpenLDAP add-on fields extraction

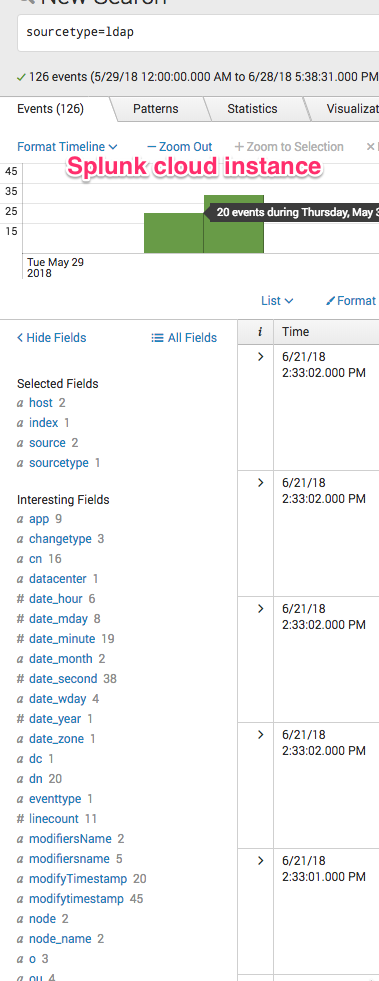
I recently installed openldap add-on on both splunk cloud instance and splunk enterprise security instance
https://splunkbase.splunk.com/app/3520/
However, the fields extraction only occurs within splunk cloud instance, not ES. How does this happen? What would be a fix for this?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

This is likely due to app-imports-update mod input not configured to accept the OpenLDAP app name:
https://docs.splunk.com/Documentation/ES/5.1.0/Install/ImportCustomApps
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I can see Splunk_TA_openldap being imported within ES when below command is performed. Seems like apps are being imported
| rest /servicesNS/admin/system/apps/local/SplunkEnterpriseSecuritySuite/import splunk_server=local | fields import
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
i assume you have done debug/refresh.
Search :
index=yourindex sourcetype=ldap modifiersname=*
try this search on both the instances.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
When your modifiedersname is searched in ES, no results get returned, while you get a bunch of data within Splunk cloud
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Can you please check Permissions for openldap add-on?
Is it Private or Global or App?
Please make it Global.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
It was set to App and I changed to Global. However, there is no difference in fields extraction.




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
