
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Admin Other
- :
- Security
- :
- Required capabilities to upload a file
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi all,
From one client is required that users, with a role similar to power, have to be able to upload files using the GUI.
With the following capabilities:
- accelerate_search
- change_own_password
- delete_messages
- edit_monitor
- edit_search_schedule_window
- edit_sourcetypes
- edit_statsd_transforms
- edit_tcp
- embed_report
- export_results_is_visible
- get_metadata
- get_typeahead
- indexes_edit
- input_file
- list_accelerate_search
- list_inputs
- list_metrics_catalog
- list_tokens_own
- metric_alerts
- output_file
- pattern_detect
- request_remote_tok
- rest_apps_view
- rest_properties_get
- rest_properties_set
- rtsearch
- run_collect
- run_mcollect
- schedule_rtsearch
- schedule_search
- search
- search_process_config_refresh
- upload_lookup_files
Users are able only to reach this point:
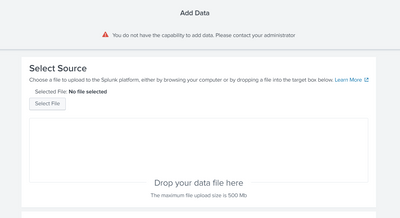
I tried to find in the docs what is the missing capability in here, but I cannot find it. Can someone give a hand on this? Many thanks in advance.
Best regards.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

As mentioned here, looks like there is no index assigned in your roles, hence the add data is showing error like this.
Go to setting->roles->Go to your role->index, assign some index to your user.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
hi @pbalbasdtt,
You need to inherit role user OR power to the new role. Looks like only Splunk default roles have access to upload file and index.
If this reply helps you, an upvote/like would be appreciated.


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
