
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: How to enable status of tokens using HTTP Even...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

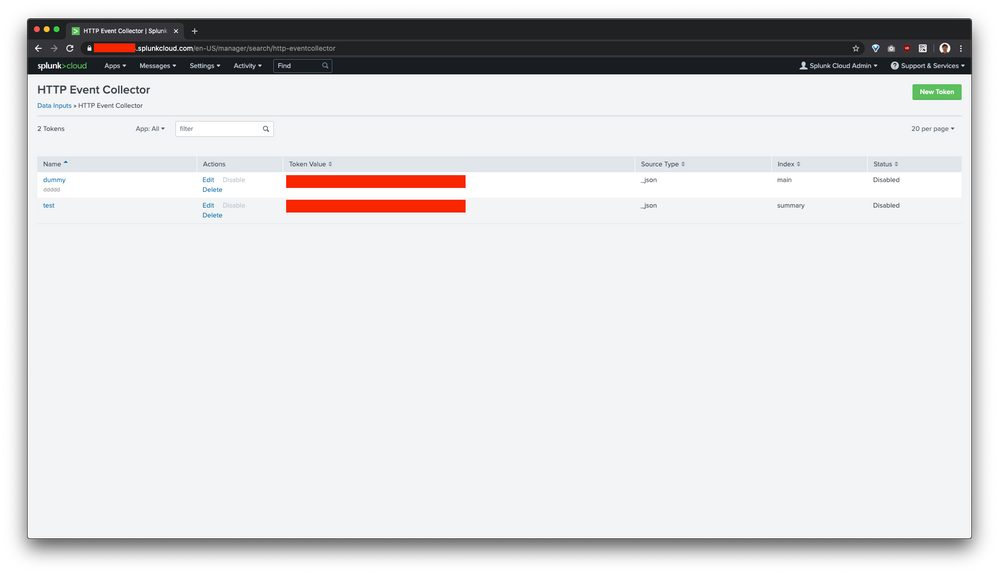
I am trying to use Splunk's HEC to ingest data. I noticed that the HEC tokens' statuses are disabled. How can I enable this to use HEC?
Also, I don't see an option to enable HEC.
I am using Splunk Free on Splunk Cloud. I don't have a license and I didn't download anything.

- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi @mjunglw
You will be very limited on a free license as the free cloud license only lasts 15 days. You would normally have a HEC creation button but with free this wont be available. Your best speaking to Splunk directly or downloading the enterprise version to run locally.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I have same problem.
Documents say use 'Global Settings' on HEC page. But, on Splunk Cloud there is not Global Settings button next to New Token.
No support on trial, so can't access Splunk support.
Seems like a pretty serious limitation since you can also not send syslog traffic to splunk cloud.
Anyway to get HEC token enabled on Splunk Coud trial?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @mjunglw
You will be very limited on a free license as the free cloud license only lasts 15 days. You would normally have a HEC creation button but with free this wont be available. Your best speaking to Splunk directly or downloading the enterprise version to run locally.




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
