
Join the Conversation
- Find Answers
- :
- Apps & Add-ons
- :
- All Apps and Add-ons
- :
- All Apps and Add-ons
- :
- Timeline - Custom Visualization: Can full date tim...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

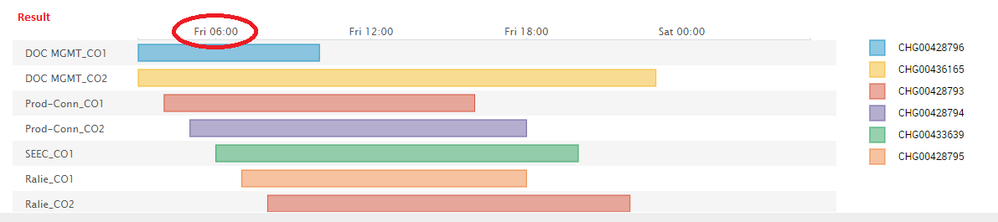
We have timelines that span 30 days with events we want to see begin/end down to the minute or second on Tool Tips.
Please add options for Tooltips time format:
DD/MM/YY HH:MM:SS
DD/MM/YY HH:MM
Cool visualization, but need more control. Also see other requests for legend and left label width control.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi @snoobzilla,
Thanks for your suggestions. I have passed your request along to our engineering team to consider for an upcoming release. Please stay tuned!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Yes!! it is possible. Make changes to two .js files as below:
- \Splunk\etc\apps\timeline_app\appserver\static\visualizations\timeline\src\timline.js
-
\Splunk\etc\apps\timeline_app\appserver\static\visualizations\timeline\visualization.js
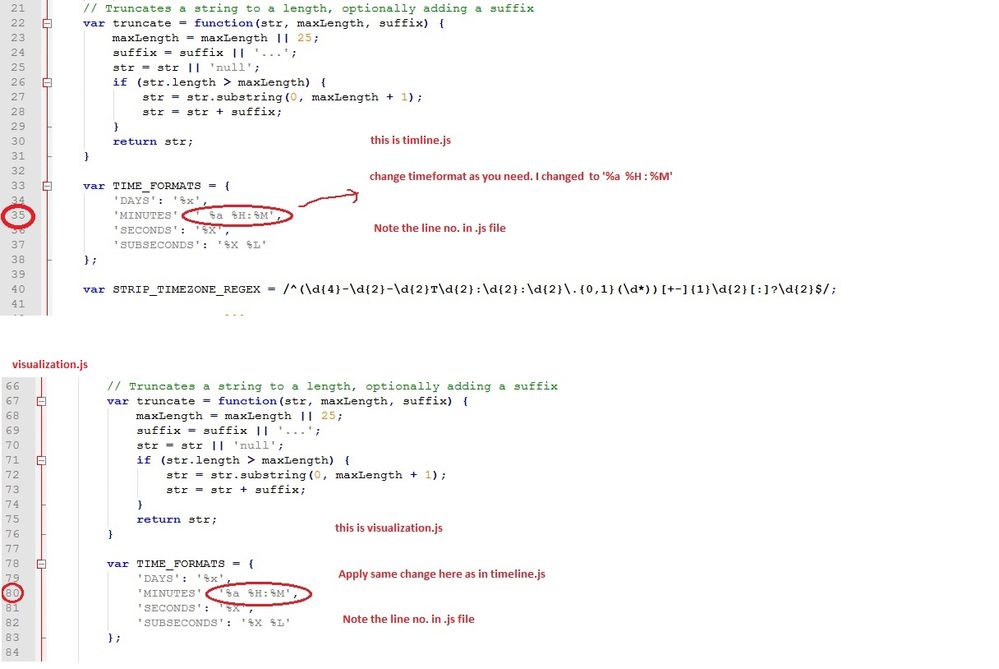
save files and Logout and re-login splunk to reflect the changes.
In this case I used '%a %H : %M' as desired time format. Any format can be used including "DD/MM/YY HH:MM"
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Yes, it is possible to add. you just need to edit the .js file for the app under location :
Splunk_HOME\etc\apps\timeline_app\appserver\static\visualizations\timeline\src\timeline.js
You'll have to play around with those locations for time_format.
Don't forget to run "npm run build" after you modify the JS. And disable caching on Splunk.
https://docs.splunk.com/Documentation/Splunk/6.5.0/AdvancedDev/CustomVizTutorial
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thanks... don't have admin access. Will be waiting for it to be added to app.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @snoobzilla,
Thanks for your suggestions. I have passed your request along to our engineering team to consider for an upcoming release. Please stay tuned!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I'd like YYYY-MM-DD HH:MM as an option, please.




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
