
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Other Using Splunk
- :
- Alerting
- :
- Alert Manager Enterprise doesn't work.
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

I was referring to this video
https://www.youtube.com/watch?v=Dv_lp-aHnv8
but no events found at the event summary page.
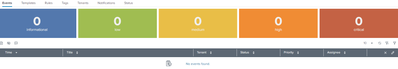
this is setup and Migration page.
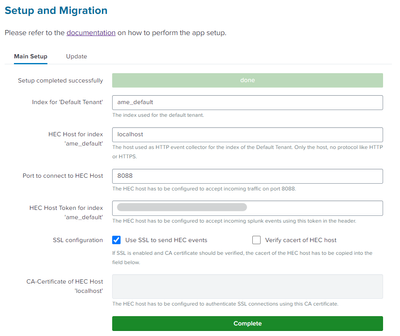
I installed Splunk in a local environment, so I filled HEC Host and Port with default values(localhost, 8088).
Please tell me if I'm doing something wrong.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @rolypolytoyy,
there's a requirement for the alerts to be visible in Alert Manager: Alerts must have a Global condivision level, otherwise they aren't visible.
Are you alert shared at Global level?
Ciao.
Giueppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @rolypolytoyy,
there's a requirement for the alerts to be visible in Alert Manager: Alerts must have a Global condivision level, otherwise they aren't visible.
Are you alert shared at Global level?
Ciao.
Giueppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I really thanks for your response!
But I solved the problem with other solution. The solution is below
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @rolypolytoyy ,
good for you, see next time!
let me know if I can help you more, or, please, accept one answer for the other people of Community.
Ciao and happy splunking
Giuseppe
P.S.: Karma Points are appreciated 😉

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Persistent Queue at TcpOut — One of Splunk's Most Practical Features
Build resilience for the agentic era: Join us at Splunk Go San Jose
Manage Edge Processor pipelines end to end with APIs
