
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: drop null value
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

I have below query
index=f5 partition="/Common/-" | rex "Username\s+'(?
username is there but first attempt he left empty and in second try he add his username. so the Username is showing null values whereas the default user field is showing actual username.
I am using coalesce because I want to take either value but it should not be null. How can I achieve this.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Function coalesce assigns the value of user field only if Username field does not exist in that event. But here it is set as empty string (""). Use if instead. below will sets value to user if Username is blank else sets to Username.
index=f5 partition="/Common/-" | rex "Username\s+'(?<Username>.*)'"| eval Username=if(Username == "", user, Username)
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

index=f5 partition="/Common/-"
| rex "Username\s+'(?<Username>\w+)'"
| eval Username=coalesce(Username, user)
your REGEX .* match null value.
How about this?
If Username has -, REGEX is [\w\-]+.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Function coalesce assigns the value of user field only if Username field does not exist in that event. But here it is set as empty string (""). Use if instead. below will sets value to user if Username is blank else sets to Username.
index=f5 partition="/Common/-" | rex "Username\s+'(?<Username>.*)'"| eval Username=if(Username == "", user, Username)
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
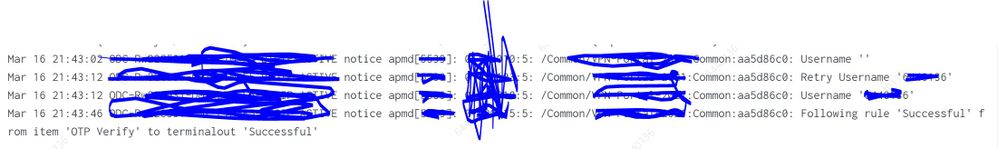
Can you provide a sample event?
It sounds like your regular expression might not be working exactly as you expect.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
attaching for your kind consideration

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Meet the .conf26 AI Agent Buildathon Winners
Trusted Autonomy in the SOC: A Maturity Journey
Supercharging Windows Security Detection Performance: Introducing Hybrid Field ...
