
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Viewstates Error when trying to save/clone/edit se...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

So we have a number of searches that cannot be saved or cloned due to viewstate errors. Many of them are accelerated and scheduled and I need to be able to edit them so that they run properly.
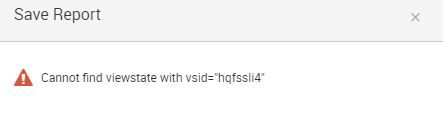
I have checked this answer HERE
I confirmed that my $SPLUNK_HOME/etc/apps/search/metadata/default.meta file has the right entry for viewstates. As shown.
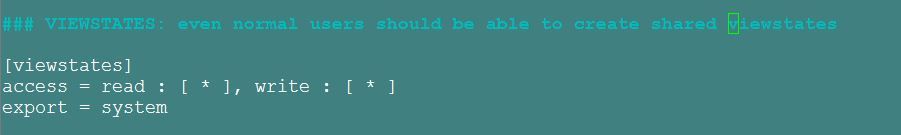
I have taken some of them and recreated them as new searches, and they saved just fine. Then I can delete them without issue.
What else might I try?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Go to the CLI on the Search Head, find the savedsearches.conf file that has the viewstate in it (if *nix, you can use find $SPLUNK_HOME/etc/ -name savedsearches.conf -exec grep -l hqfssli4 {} \;). Stop splunk, edit the file and REMOVE the viewstate line entirely, save it, restart splunk, enjoy. Make a backup of the file first.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Go to the CLI on the Search Head, find the savedsearches.conf file that has the viewstate in it (if *nix, you can use find $SPLUNK_HOME/etc/ -name savedsearches.conf -exec grep -l hqfssli4 {} \;). Stop splunk, edit the file and REMOVE the viewstate line entirely, save it, restart splunk, enjoy. Make a backup of the file first.




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
