
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: User agent string using lookup table
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
User agent string using lookup table

Hi Team
I am trying to extract the OS details from the user agent using the below eval command, however I am not able to see new filed was created (test) after i executed the spl query
index=aws Website="*"
| eval test = case(match(useragent,"Windows .. 5\.1"),"Windows XP",match(useragent,"droid"),"Android",match(useragent,"Windows NT 6.1"),"Windows 7")
Any help please
Thank s
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi richgalloway
Thanks for your message
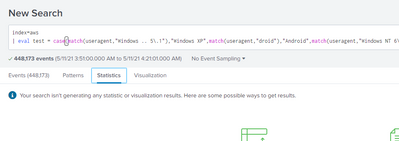
Yes, i tried executing's the SPL command found no error however i am not getting any statistics result
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


The query you ran does not have a command that generates statistics so you won't see anything in the Statistics tab. Look at the results in the Events tab or add commands to the given query. It was not meant to be complete - just to answer the question asked.
If this reply helps you, Karma would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
The case function will return null if none of the expressions are true. That's why it's a good practice to include as the last expression something that will always evaluate to true (similar to the 'default' case in HLLs).
index=aws Website="*"
| eval test = case(match(useragent,"Windows .. 5\.1"),"Windows XP",match(useragent,"droid"),"Android",match(useragent,"Windows NT 6\.1"),"Windows 7", 1==1, "Unknown")
If the field is set to the default value then you know none of the other cases matched and you need to re-evaluate your code.
If this reply helps you, Karma would be appreciated.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Persistent Queue at TcpOut — One of Splunk's Most Practical Features
Catalog Is Now Generally Available on Splunk Cloud Platform
Your Path to AgenticOps: AI Experiences for Every Splunk Practitioner
