
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Translation lookup table
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I have extraction of a field called Tool (Textual)
The field values can be in English, German, French or Spanish.
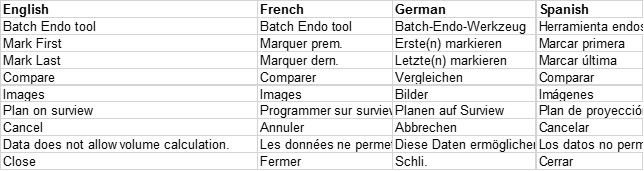
I have a lookup table that contains all the options of this values in all those languages (see attached example)
I want to create a field called TranslatedTool that any event will be translated into english
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

If every string everywhere is completely unique (exceedingly likely), then you can do it like this with successive lookups:
... | lookup ToolLookup English AS Tool OUTPUT English AS TranslatedTool
| lookup ToolLookup French AS Tool OUTPUT English AS TranslatedTool
| lookup ToolLookup German AS Tool OUTPUT English AS TranslatedTool
| lookup ToolLookup Spanish AS Tool OUTPUT English AS TranslatedTool
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

If your event data includes a mixture of languages, a straightforward approach is to restructure your reference table. In this new setup, the first column should encompass all conceivable combinations of "Tools" values, including English. The second column should store the corresponding English translations for each item, denoted as "TranslatedTool."
With this arrangement in place, you can effortlessly incorporate a lookup command into your search process or establish an automated lookup mechanism to generate the "TranslatedTool" field, featuring the accurate English translations.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
If every string everywhere is completely unique (exceedingly likely), then you can do it like this with successive lookups:
... | lookup ToolLookup English AS Tool OUTPUT English AS TranslatedTool
| lookup ToolLookup French AS Tool OUTPUT English AS TranslatedTool
| lookup ToolLookup German AS Tool OUTPUT English AS TranslatedTool
| lookup ToolLookup Spanish AS Tool OUTPUT English AS TranslatedTool
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

If your events contain mixed languages, the easiest would be to rearrange your lookup table to have column one be all possible permutations of the values for "Tool" (including English) and have column 2 be the English translation for each (TranslatedTool).
Then you can just add a lookup command to your search or define an automatic lookup to create the field TranslatedTool with the proper English translation.



Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Rounding off the Splunk Dashboard Contest
A Four Part Event Series: AI + Observability: AI Agents, LLMs, Apps, & Infrastructure
