
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Timechart and overlay two columns?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

I have a field outcomeIndicator in my data, that holds values 0,1,5,8.
0 and 1 mean a success of the event, and 5 and 8 mean failure.
Now, I want to use timechart count to plot these values over a month, for a span of 1 day, i.e the timechart must show the total events in a day resulting in success and failures, for the previous 30 days.
This timechart must strictly be graphical and must show the trend for both failures and successes over a month.
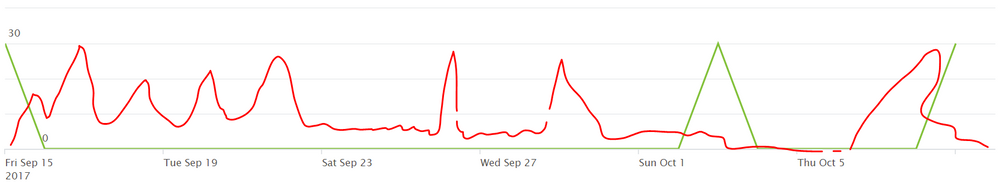
Here the green colored trend-line represents the success per day for a month and the red colored trend-line represents failures per day over a month. The image is just for representation and I want to know the possibilities of achieving this.
Thank you.
Cheers.
-Snipedown21
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi snipedown21,
try something like this:
your_search
| eval result=if(outcomeIndicator<2,"Success","Failure")
| timechart count by result
To set the green and red colors use
<option name="charting.legend.labels">[Success,Failure]</option>
<option name="charting.seriesColors">[0x008000,0xFF0000]</option>
Bye.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi Giuseppe.
Dude!!! That was absolutely perfect. Even the color schemes I had put up in the sample were exactly what you gave me.
Thank you a lot.



Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Vibe-coding, AI, and Splunkcraft: Highlights from the .conf26 Builder Bar
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
