
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: ForEach value in table
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How to search ForEach value in table

I would like to search for each value in an extracted field.
My intial query is as follow:
index=moneta-pro "IPN Post API execution started for the orderRefNo" AND "printOs" | rex field=_raw "(?ms)^(?:[^ \\n]* ){9}(?P<orderId>\\d+)" offset_field=_extracted_fields_boundsd_fields_bounds | table orderId | dedup orderId
which returns following:
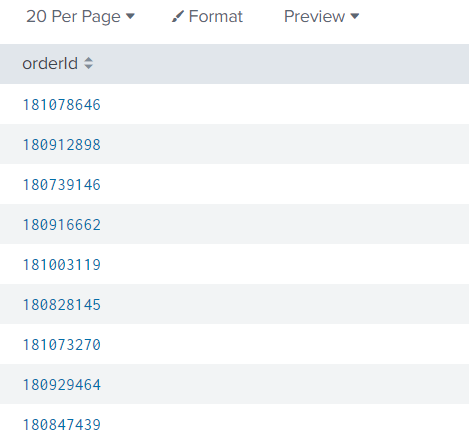
Now I'd like to use each value in OrderId and use it in search and append to the above table. For example, check the status of the order. Individual query should look like.
index=* " Received response status code as 200 and the message body as" AND orderId=<<each dynamic value from above table>>
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Make the first search a subsearch to the second, i.e.
index=* " Received response status code as 200 and the message body as" [
  search index=moneta-pro "IPN Post API  execution started for the orderRefNo" AND "printOs"
  | rex field=_raw "(?ms)^(?:[^ \\n]* ){9}(?P<orderId>\\d+)" offset_field=_extracted_fields_boundsd_fields_bounds
  | fields orderId
  | dedup orderId
]
Note the use of fields, not table (fields is more efficient in that it can run on the indexer, whereas table will always run on the search head.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

In general, your remark is of course correct and hundred percent valid. But in this case I suppose it doesn't make much of a difference since the subsearch results have to be returned to the search-head initiating the search so it can compose the main search with the subsearch results to have a full search for dispatching to search peers.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
It makes a difference in that the original ordering was table + dedup, hence the duplicates would be sent to the SH before being deduped.
I don't know how splunk manages the distribution of multiple searches and whether it has to dispatch each search separately - I've never delved into that too deeply
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Here you are right. I rarely use dedup as such (I'm mostly a "stats values" kinda guy ;-)). You could change the order of commands (dedup | table) but then again fields | dedup is more elegant, I agree.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Agreed on dedup! It seems somewhat nondeterministic. Makes more sense to use stats


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
