
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Convert time format
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi,
i need to write a query that converts time format from
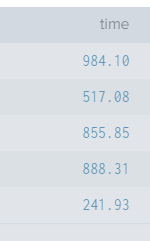
my query
| eval finish_time_epoch = strftime(strptime(FINISH_TIME, "%Y-%m-%d %H:%M:%S"),"%Y-%m-%d %H:%M:%S")
| eval start_time_epoch = strftime(strptime(START_TIME, "%Y-%m-%d %H:%M:%S"),"%Y-%m-%d %H:%M:%S")
| eval duration_s = strptime(FINISH_TIME, "%Y-%m-%d %H:%M:%S") - strptime(START_TIME, "%Y-%m-%d %H:%M:%S")
| eval duration_min = round(duration_s / 60, 2)
| chart sum(duration_min) as "time" by Yd_count_data
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @Edwin1471,
if "time" is the duration expressed in minutes, you have to add at the end of your search an eval statement like the following:
|  eval
   time_hours=round(time/60,0),
   time_min=round(time-time_hours*60,0),
   time_sec=round((time-time_hours*60-time_min)*60,0)
| eval time=time_hours." h ".time_min." m ".time_sec
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @Edwin1471,
if "time" is the duration expressed in minutes, you have to add at the end of your search an eval statement like the following:
|  eval
   time_hours=round(time/60,0),
   time_min=round(time-time_hours*60,0),
   time_sec=round((time-time_hours*60-time_min)*60,0)
| eval time=time_hours." h ".time_min." m ".time_sec
Ciao.
Giuseppe


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Vibe-coding, AI, and Splunkcraft: Highlights from the .conf26 Builder Bar
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
