
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- How to Add percentage to Column?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi
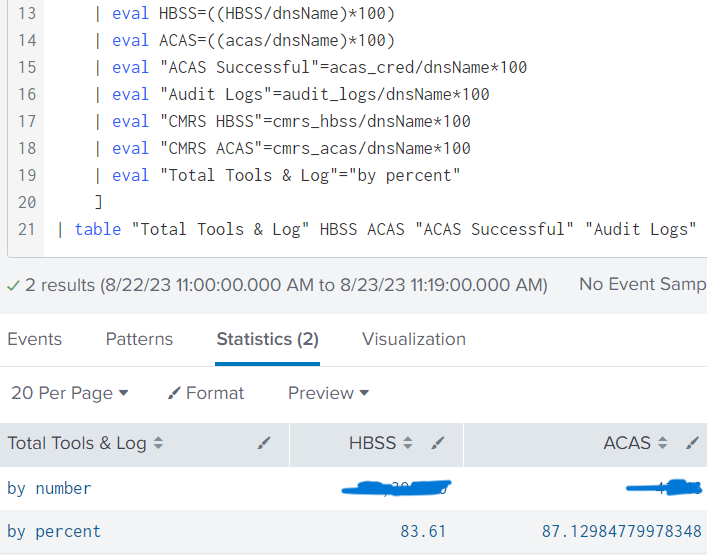
I am trying to add % to the "by percent" column only. I can't seem to get it to show.
Thanks
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @woodlandrelic,
please next time, add to your question also the code in text format (using the Insert/Edit Code Sample button), so we don't have to rewrite the code!
Anyway,, before the table command you should add an eval command like the following
<your_search>
| eval HBSS=HBSS."%", ACAS=ACAS."%"
if you want you could also round the results e.f. to the second decimal:
<your_search>
| eval HBSS=round(HBSS,2)."%", ACAS=round(ACAS,2)."%"
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @gcusello
My apologies, I will do that next time.
This is how I got it to work because I needed to still divide by "dnsName"
| eval HBSS=round(HBSS/dnsName*100)."%"
Thank you
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @woodlandrelic ,
good for you, you're always welcome! see next time!
Ciao and happy splunking
Giuseppe
P.S.: Karma Points are appreciated 😉


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
