
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: DB Query
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
DB Query

Hi All,
Can someone advice what is wrong with this following query.
|dbquery wmsewprd "select * from sys_code_type where rec_type='C'" when I run this ,I get an error.
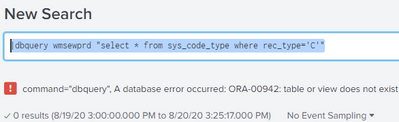
But when I use wmsew.sys_code_type instead of sys_code_type I get the exact output.Can any help me this.Our requirement is to work |dbquery wmsewprd "select * from sys_code_type where rec_type='C'" .
wmsewprd -- External Database.
Regards,
Rahul
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


I don't understand why, when you know the syntax that works, you insist on using syntax that does not work.
If you need to use a different name later in your query then you use rename wmsew.* as *.
If this reply helps you, Karma would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @richgalloway ,
Could you please elaborate more about this:
If you need to use a different name later in your query then you use rename wmsew.* as *.
Regards,
Rahul
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
You said this query fails
|dbquery wmsewprd "select * from sys_code_type where rec_type='C'and this one does not
|dbquery wmsewprd "select * from wmsew.sys_code_type where rec_type='C'So I presume you wish to refer to the sys_code_type field by that name. You can do that, but first you must comply with the database's name rules and include the table name in the query. After that, if necessary, you can use rename to strip out the table name from fields.
|dbquery wmsewprd "select * from wmsew.sys_code_type where rec_type='C'
| rename wmsew.* as *
If this reply helps you, Karma would be appreciated.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Splunk Enterprise Security: An Automated Phishing Response Workflow
Sharper ES Detections, Agentic AI Integrations, Smarter Workload Management, and More ...
Data Outage Monitoring and Reporting
