
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Append static data to a field for charting
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hello,
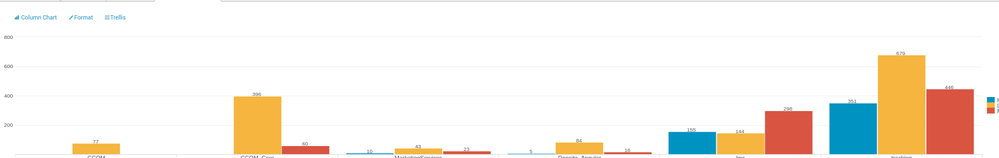
I am trying to append static data to a chart that splunk generates and i'm not sure how to do this with a lookup or anything. The end goal is to have additional x-axis entries (ProjectNames) on my chart with arbitrary values for Severity, alongside the actual real data found in our splunk index. Here is what it currently looks like:
index=myindex
| rename CxXMLResults.@ProjectName as ProjectName
| rename CxXMLResults.@Team as Team
| rename CxXMLResults.Query.Result.@Severity as Severity
| rename CxXMLResults.Query.Result.Path.@PathId as PathId
| eval deduper=md5(Team.ProjectName.PathId)
| dedup deduper
| fillnull value=''
| append [eval ProjectName="MyArbitraryProject"]
| chart count(Team) over ProjectName by Severity
in the |append [eval ProjectName="MyArbitraryProject"] I Am trying to make a new project called "MyArbitraryProject" that will show up on the X axis, but obviously this doesn't work because I dont have Severity values available for it. Please help! I'm stumped.

- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Close. Once I discovered | makeresults thanks to @HiroshiSatoh I ended up with this that works
...
| dedup deduper
| fillnull value=''
| append [| makeresults count=1000 | eval ProjectName="MyArbitraryProject" | eval Team="MyTeam" | eval Severity="UNKNOWN" ]
| chart count(Team) over ProjectName by Severity
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Give this a try
index=myindex
 | rename CxXMLResults.@ProjectName as ProjectName
 | rename CxXMLResults.@Team as Team
 | rename CxXMLResults.Query.Result.@Severity as Severity
 | rename CxXMLResults.Query.Result.Path.@PathId as PathId
 | eval deduper=md5(Team.ProjectName.PathId)
 | dedup deduper
 | fillnull value=''
 | chart count(Team) over ProjectName by Severity
 | fillnull value=0
 | append [| makeresults |eval ProjectName="MyArbitraryProject"]
 | fillnull value=500
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Just want to add one row?
| append [| makeresults |eval ProjectName="MyArbitraryProject",Severity="your Severity"]
| chart count(Team) over ProjectName by Severity
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
This almost did what I need to.. the Count isn't showing up on the chart though. i.e.
index=checkmarx
CxXMLResults.Query.Result.@state!=1
CxXMLResults.Query.Result.@Severity!=Information
| rename CxXMLResults.@ProjectName as ProjectName
| rename CxXMLResults.@Team as Team
| rename CxXMLResults.Query.Result.@Severity as Severity
| rename CxXMLResults.Query.@name as VulnName
| rename CxXMLResults.Query.Result.Path.@PathId as PathId
| eval deduper=md5(Team.ProjectName.PathId)
| dedup deduper
| fillnull value=''
| append [| makeresults | eval ProjectName="MyArbitraryProject", Severity="High", count=500]
| chart count(Team) over ProjectName by Severity

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Make your Splunk investment work harder with Optimization Advisor
How Splunk AI Assistant Is Transforming Investigations: Insights from .conf26
Make Your Machine Data AI-Ready in Splunk
