
Join the Conversation
- Find Answers
- :
- Splunk Products
- :
- Splunk SOAR
- :
- Deleting Custom List Items
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

In a playbook, I have a decision tree.
If option A -> Check List -> If Value Exists in custom list -> Do Nothing
Else If Option b -> Check list -> If Value Exists in custom list -> Delete that list entry.
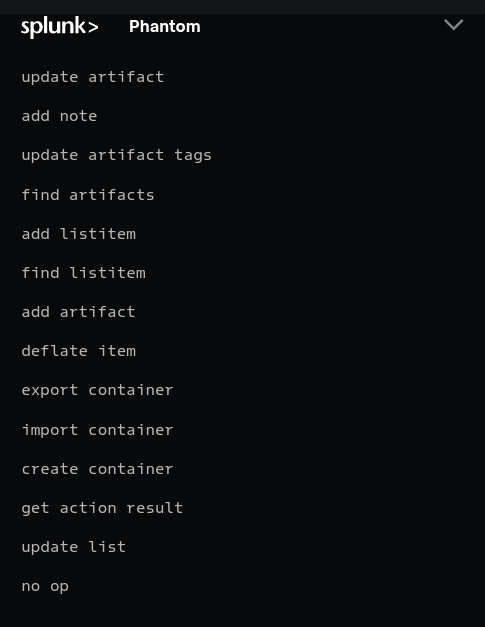
Checking in the SOAR Phantom app actions, I see several options for lists, but no option to "remove/delete listitem" (see attached pic)
How do I go about deleting items from a Custom List?
Thanks!
(SOAR Cloud 5.3.1)
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


There is an API to perform this in a code block or custom function:
https://docs.splunk.com/Documentation/SOAR/current/PlaybookAPI/DataManagementAPI#delete_from_list
Otherwise you can rebuild the list without the value(s) and then use set_list to overwrite:
https://docs.splunk.com/Documentation/SOAR/current/PlaybookAPI/DataManagementAPI#set_list
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
There is an API to perform this in a code block or custom function:
https://docs.splunk.com/Documentation/SOAR/current/PlaybookAPI/DataManagementAPI#delete_from_list
Otherwise you can rebuild the list without the value(s) and then use set_list to overwrite:
https://docs.splunk.com/Documentation/SOAR/current/PlaybookAPI/DataManagementAPI#set_list
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
Announcing Modern Navigation: A New Era of Splunk User Experience
