
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Splunk Development
Splunk Development
×
Join the Conversation
Without signing in, you're just watching from the sidelines. Sign in or Register to connect, share, and be part of the Splunk Community.
- Find Answers
- :
- Apps & Add-ons
- :
- Splunk Development
Options
Category Activity
 | Hello, I'm attempting to use a drilldown to search. The original search renamed some fields in order to improve the ... by brandonworkenti New Member in Splunk Dev 12-31-2017 0 3 | 0 | 3 | |
| | I have a python script that queries a mongo database and pulls all the results since the last time the script ran. it... by bkwoka Explorer in Splunk Dev 12-31-2017 0 2 | 0 | 2 | |
 | I have found many answers but none seem to satisfy what I am trying to accomplish. I am looking through some juniper... by martincd537 New Member in Splunk Dev 12-29-2017 0 3 | 0 | 3 | |
| | We just upgraded from v6.4 to v7.0.1 and now I am getting an error when trying to use the TableView component on a da... by skisoccer13 Explorer in Splunk Dev 12-29-2017 1 5 | 1 | 5 | |
 | I am having the comments field with the data below: 'ADP-ECS~FILEMANIFEST~20171228-221014~60.txt.gz and ADP-ECS~FILE... by karthi25 Path Finder in Splunk Dev 12-29-2017 0 2 | 0 | 2 | |
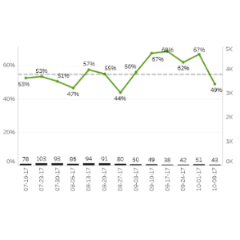 | I want two y-axis graph having percentage on left side and number (in thousands) on right side.And on x axis we shoul... by sxp5686 Explorer in Splunk Dev 12-29-2017 0 3 | 0 | 3 | |
| | Hi , I am developing a new App using Splunk Java SDK. My use-case requires writing data to index directly. To do t... by dileepmandapam New Member in Splunk Dev 12-28-2017 0 6 | 0 | 6 | |
| | I found a document saying you can create multiple data series here: http://docs.splunk.com/Documentation/Splunk/lates... by yww325 New Member in Splunk Dev 12-28-2017 0 3 | 0 | 3 | |
 | Hello. How best to implement Patch Management in Splunk for Win\Linux? Maybe some blogs, articles, APPs that can help... by test_qweqwe Builder in Splunk Dev 12-28-2017 0 7 | 0 | 7 | |
| | I installed the OpsGenie integration for Splunk and set the API key during initial configuration within the Splunk we... by bschaap Path Finder in Splunk Dev 12-28-2017 0 2 | 0 | 2 | |
| |  Splunk collecting security solusion logs that is DefensPro. I want to extract fields. Log samples are.. Dec 26 15... by superhm Explorer in Splunk Dev 12-26-2017 0 5 | 0 | 5 | |
| | I am trying out Splunk on Windows Server 2012, version 6.6.3 and attempting to do a scripted lookup with a python scr... by po1splunk New Member in Splunk Dev 12-18-2017 0 2 | 0 | 2 | |
| | Hi! I'm reading the scripted input documentation but I don't understand if they can help me in what I'd like to do. ... by drebai Explorer in Splunk Dev 12-14-2017 0 3 | 0 | 3 | |
| | Hi! I created a custom command for a comparison between json. The steps to create it: 0) created fieldcompare folder... by drebai Explorer in Splunk Dev 12-13-2017 0 8 | 0 | 8 | |
 | Hello, I am trying to get a very simple python scripted input to work, but I cannot. I am using Splunk 6.6.3 runnin... by andrewtrobec Motivator in Splunk Dev 12-13-2017 0 9 | 0 | 9 | |
 | I can't find documentation anywhere on how to format search strings for the Splunk SDK. Every single example provided... by scottmacdonald New Member in Splunk Dev 12-12-2017 0 3 | 0 | 3 | |
 | Hi All, Currently we are facing an problem in time stamp for a Symantec log data. Problem: When we search with the b... by Hemnaath Motivator in Splunk Dev 12-11-2017 0 36 | 0 | 36 | |
 | I Have Two Queries That Both Work In Splunk Web Ui This Query Works In Web UI BUT NOT In Api I Probaly Have A Syntax... by charles_corder New Member in Splunk Dev 12-07-2017 0 1 | 0 | 1 | |
| | I tried to pass sampleRatio parameter in JobsArgs, but no luck. Is there any way to set sampling ratio in Splunk job? by ashiqm Explorer in Splunk Dev 12-04-2017 1 3 | 1 | 3 | |
 | Hi Splunk, I am trying to create splunk search in my python script where the script is being used to create HPSM tic... by thambisetty SplunkTrust  in Splunk Dev 12-01-2017 0 5 | 0 | 5 | |
 | How can I concatenate multiple variables in SplunkJS script? e.g: var date = Date.now(); var alertid = 12345; var fi... by clement Explorer in Splunk Dev 11-30-2017 0 1 | 0 | 1 | |
| | Is it possible to read SSO configuration summary via a custom command?(Written in Python using Splunk Lib) such as Tr... by madhukarhebbar Engager in Splunk Dev 11-30-2017 0 1 | 0 | 1 | |
| | I have a set of files that need some processing before indexing with Splunk. The multi line events can be broken out ... by kuokhoet New Member in Splunk Dev 11-27-2017 0 1 | 0 | 1 | |
| | I understand there's no way to do field extraction based on event types, but is there a way to COPY (not move) events... by aworkman Engager in Splunk Dev 11-24-2017 1 4 | 1 | 4 | |
| | Just wondering where the API is for the python module splunk.Intersplunk (used for making scripts that work on stream... by Jason Motivator in Splunk Dev 11-18-2017 5 3 | 5 | 3 |
Splunk Learning
Splunk has training and education options for everyone, whether it's your first or fiftieth deployment.
Announcements
Register for Upcoming Live Tech Talks! Security, Observability, Platform and App Developer Editions are held every month.
Get Updates on the Splunk Community!
Make Your Machine Data AI-Ready in Splunk
Every team is getting ready for AI agents.
Watch On-Demand
In this Tech Talk, Splunk platform specialists ...
How to Break a Kubernetes Pod on Purpose and Let the AI Troubleshooting Agent Find ...
Let's say I've just rolled out a Kubernetes Deployment with a typo in the image tag. Nothing explodes. The pod ...
Splunk Add-on for Microsoft Windows 11.0.3: Parse Once, Search Faster
The updated Splunk Add-on for Microsoft Windows helps customers search Windows events faster by reducing ...

