
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Splunk Dev
×
Join the Conversation
Without signing in, you're just watching from the sidelines. Sign in or Register to connect, share, and be part of the Splunk Community.
- Find Answers
- :
- Apps & Add-ons
- :
- Splunk Development
- :
- Splunk Dev
- :
- Re: Getting error while adding ServiceNow incident...
Options
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Getting error while adding ServiceNow incident through Splunk add-on: "Failed to create ticket..."

smitra_cis
Observer
07-21-2020
04:10 PM
Hello
I am getting the following error while inserting the incident in ServiceNow through Splunk Add-On (while the connectivity between Splunk and ServiceNow is established, able to retrieve the incidents in Splunk)
command="snowincidentstream", Failed to create ticket. Return code is 400 (Bad Request). One of the possible causes of failure is absence of event management plugin or Splunk Integration plugin on the ServiceNow instance. To fix the issue install the plugin(s) on ServiceNow instance.Search
source="cpu_data_updated_1.csv" |where CPU___Usage >= 47|eval contact_type="email"
| eval account="splunk_snow_dev"
| eval contact_type="email"
| eval custom_fields="u_affected_user=nobody||u_caller_id=12345"
| eval ci_identifier=host
| eval priority=1 | eval category="Software"
| eval subcategory="database"
| eval short_description="CPU on ". host ." is at ". CPU___Usage
| table account, category, subcategory, short_description, contact_type, custom_fields, ci_identifier, priority |snowincidentstream
------------
Getting this even after installing both the plugins and following the instructions in the link: - https://docs.splunk.com/Documentation/AddOns/released/ServiceNow/ConfigureServiceNowtointegratewithS...
Regards
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
kdroddy
Explorer
07-25-2020
10:29 AM
Hello,
When you go to ServiceNow, under "Installation Checklist":
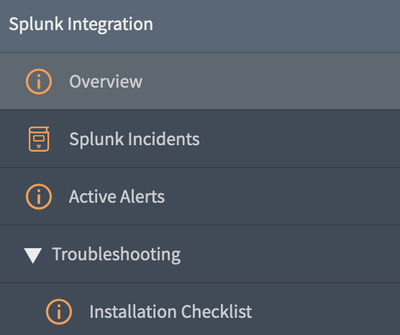
Are the appropriate steps list as "Complete" under "Task Status"?

Got questions? Get answers!
Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Meet up IRL or virtually!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Get Updates on the Splunk Community!
Splunk Asynchronous Forwarding Explained
Splunk asynchronous forwarding is often misunderstood as simply setting autoLBVolume. That is not quite right. ...
How to Monitor AI Agents with Splunk Agent Observability
Let’s say I’m running a travel planning AI app in production. A user asks for three concise hotel options in ...
Deep Dive: The Agentic SOC in Action with Enterprise Security Agents
Takeaways:
Splunk Enterprise Security brings Agentic SOC capabilities into the analyst workflow. Agents ...
