
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Other Using Splunk
- :
- Other Usage
- :
- Re: Windows event log Splunk HF with truncation
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Windows event log Splunk HF with truncation

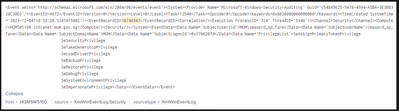
We are using Splunk Universal Forwarder (UF) to forward logs from a Windows server to a Splunk Heavy Forwarder (HF). However, when the Splunk HF receives logs of a specific type as multiline, an issue arises. In this case, when attempting to forward these logs from the Splunk HF to a syslog server (a Linux server with rsyslog configuration), the logs are getting truncated. How can we address and resolve this issue?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @sarvananth,
Have you reviewed rsyslog documentation for maximum message length and line endings? If you're forwarding using a syslog output over UDP, the transport itself has a limit of 65,535 bytes per datagram (subtract headers for maximum payload length). You may also want to transform the events by replacing line endings with an escape sequence of your choosing (or one required by the consumer).
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

The screenshot shows an untruncated event. What makes you believe the logs are getting truncated? Please show a sanitized sample truncated event.
Why are the events going from a Splunk HF to a syslog server instead of to a Splunk indexer?
If this reply helps you, Karma would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
please check the truncated event from syslog server

We are attempting to send logs to both the Splunk indexer and the syslog server because different teams handle distinct log types. My team manages the system security logs specifically for SOC team monitoring.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

This can be caused by syslog not supporting newlines(\n).
The following settings on the HF will improve this.
props.conf

[your-sourcetype]
TRANSFORMS-◯◯ = transname

transforms.conf

[transname]

INGEST_EVAL = _raw=replace(_raw, "\n", " ")

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
