
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: time field search in load job not working
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
time field search in load job not working

Hi,
I have a savedsearch which i am calling like below.
| loadjob savedsearch="admin:Splunk_Security:chk_coding_pie_accl" |search Time="*2020-08-24*"
When i have to use Time tokens then its not working
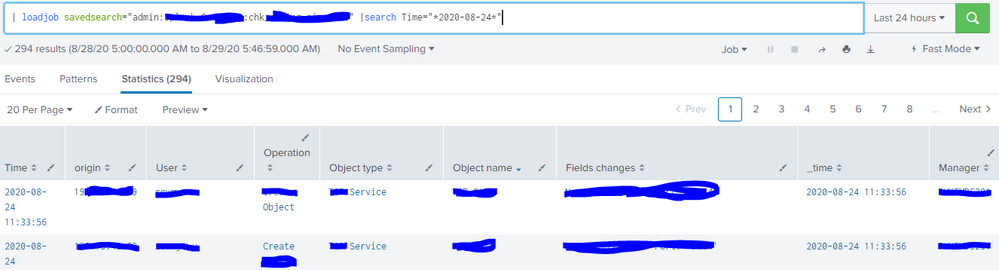
This loadjob query is my pie chart query for a panel where earlist time and latest time will be as per the choosen time from the time field.
Now when i try to pass this like below i get no results although it has value for that Time.
|loadjob savedsearch="admin:appname:savedsearch" |search earliest=$field1.earliest$ latest=$field1.latest$ | stats count by Manager
How to pass the time properly here ?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


First, convert your Time field using below eval Time_epoch and then you need to pass your value in where in epoch time.
|makeresults | eval _raw="Time,user
2020-08-24 12:50:14,admin
2020-09-01 12:40:14,power"
| multikv forceheader=1
| table Time user
| eval Time_epoch=strptime(Time,"%Y-%m-%d %H:%M:%S")
| where Time_epoch<=1598259014If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
you should pass something like below:
| search earliest=“” latest=“”
the format of earliest and latest is
%m/%d/%Y:%H:%M:%S
https://docs.splunk.com/Documentation/Splunk/8.0.5/SearchReference/SearchTimeModifiers
If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @thambisetty
I understand that i have to change the format but it doesn't work as expected. I added the where clause but looks like that doesn't work.
| where Time=strptime("1599503400","%Y-%m-%d %H:%M:%S")


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
Announcing Modern Navigation: A New Era of Splunk User Experience
