
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- strangely Behaviuor with Sourcetype
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
strangely Behaviuor with Sourcetype
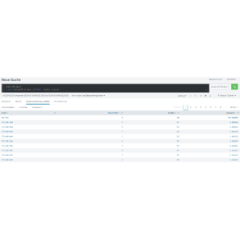
I have installed a universal Forwarder on Microsoft Exchange Server and it had starting to send the data from the log files to Splunk Server. I have configured two types of Sourcetype (SEND,RECV) but strangely they became four (SEND,send-too_small,RECV,recv-too_small) and after that it had not indexed the data under SEND or RECV spurcetypes!!!!
I don't know why it's happing. Anyone have an idea!!
Thanks for help 🙂
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi
Splunk assigns that sourcetype to files which are having less than 100 lines or 100 events in file.
Check the PREFIX_SOURCETYPE in props.conf
Thanks
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


The "-too_small" suffix indicates Splunk has found data which it could not match to any provided sourcetype. Make sure you have defined a sourcetype for all of the events you expect to index. Share you props.conf settings here if you need help.
If this reply helps you, Karma would be appreciated.


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
Announcing Modern Navigation: A New Era of Splunk User Experience
