
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: multi-select parameter on a dashboard
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

I have a multi-select parameter on a dashboard.
I want to pass it to the search in the panel…a single value is …. | search myfield=”$mytoken$”
…what if I want to use a multi-value thus generate .... | search myfield=this OR myfield=that, etc.
Thanks!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

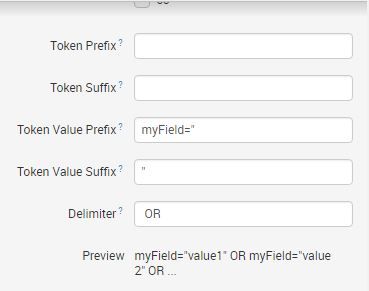
Try to use Token Value Prefix , Token Value Suffix and Delimiter option like below and later on use as your query | search $mytoken$
Notice the preview value and use accordingly in your search making sure Delimiter has the spaces around OR to get appropriate result.


- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Try to use Token Value Prefix , Token Value Suffix and Delimiter option like below and later on use as your query | search $mytoken$
Notice the preview value and use accordingly in your search making sure Delimiter has the spaces around OR to get appropriate result.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Enterprise Security Watch Party: What’s New in 8.8 - Recap
Move CrowdStrike FDR ingestion to Data Inputs with a guided migration
Make Your Machine Data AI-Ready in Splunk
