
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: Time_PREFIX for Props.conf with unstructured t...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Time_PREFIX for Props.conf with unstructured text file

Hi There,
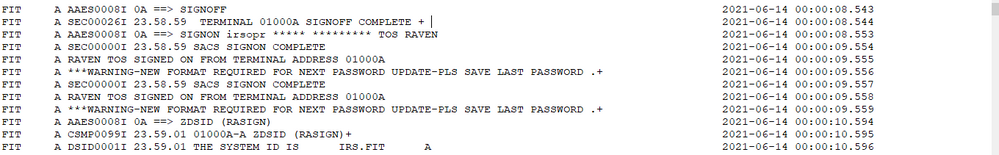
Here is a segment of my sample data . Data is in text format. My Props.conf file has also been provided below. I have some issues to figure out what I would write in TIME_PREFIX for my PROPS.Conf file (please see below). Any help will be highly appreciated, thank you.
SHOULD_LINEMERGE=false
LINE_BREAKER=([\r\n]+)
CHARSET=UTF-8
TIME_PREFIX=
TIME_FORMAT=%Y-%m-%d %H:%M:%S.%3N
MAX_TIMESTAMP_LOOKAHEAD=18
Thank you and Regards,
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @SplunkDash
I do not find a possibility to set TIME_PREFIX for your case i would rather leave the timestamp detection to Splunk, splunk is able to detect if you do not set any TIME* related conf.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Then what would be my PROPS.CONF file........
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
@SplunkDash Test with following and see how timestamp is being set by Splunk. Additionally you can set TZ which is a timezone if your event timezone is different from indexer.
SHOULD_LINEMERGE=false
LINE_BREAKER=([\r\n]+)----
An upvote would be appreciated and accept solution if it helps!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thank you so much, appreciated!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
@SplunkDash please accept solution if it helps!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @SplunkDash
Its bit tricky to find from screenshot only prefix of time you have is space which is \s, you can try something as follows, you shall change other params as well. If your text event having pre-determined spaces before timestamp just use the exact number.. something like if you have fixed 10 spaces \s{10}.
TIME_PREFIX = \s{6,}
MAX_TIMESTAMP_LOOKAHEAD = 23
TIME_FORMAT = %Y-%m-%d %H:%M:%S.%3Q
----
An upvote would be appreciated and accept solution if it helps!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi venkatasri,
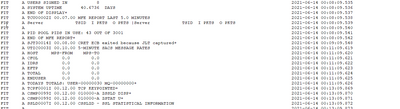
Thank you for your quick response, appreciated. Unfortunately, it's not a fixed space...it varies from 2 to 20+.... please see another segment of sample data.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Manage Edge Processor pipelines end to end with APIs
Splunk Brings Proof of Control to Digital Asset Transfers
Manage Ingest Processor pipelines end to end with APIs
