
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: Splunk - Rest API - Curl - Failing with Unbala...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Splunk - Rest API - Curl - Failing with Unbalanced Quotes

Hi,
I'm trying to write data to outputlookup file by doing a REST API Call (by running a search query).
The below command works and writes data to outputlookup csv file when running the search directly from Splunk.
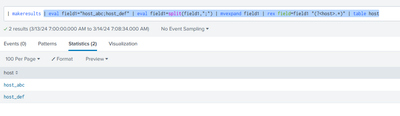
| stats count as field1 | eval field1="host_abc;host_def" | eval field1=split(field1,";") | mvexpand field1 | rex field=field1 "(?<host>.*)" | table host | outputlookup test_maintenance.csv
But this is not working when executing the above search using REST API.
Getting the below error "Unbalanced quotes" when running the below command
curl -k -u admin:admin https://splunksearchnode:8089/servicesNS/admin/search/jobs/export -d search="| stats count as field1 | eval field1=\"host_abc;host_def\" | eval field1=split(field1,\";\") | mvexpand field1 | rex field=field1 \"(?<host>.*)\" | table host | outputlookup test_maintenance.csv"
Getting the below error when running the below command
Error : Error in 'EvalCommand': The expression is malformed. An unexpected character is reached at '\'host_abc'.</msg></messages></response>
curl -k -u admin:admin https://splunksearchnode:8089/servicesNS/admin/search/jobs/export -d search='| stats count as field1 | eval field1=\"host_abc;host_def\" | eval field1=split(field1,\";\") | mvexpand field1 | rex field=field1 \"(?<host>.*)\" | table host | outputlookup test_maintenance.csv'
Appreciate your help.
Thank you

- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi Maries,
Please try with the below search
<your curl command> -d search= "search index=<indexname> | stats count as field1 | eval field1="dallvcflwb110u,yes;dallvcflwb120u,yes" | eval field1=split(field1,";") | mvexpand field1 | rex field=field1 \"(?<host>.*),(?<mode>.*)\" | table host mode | outputlookup atlassian_maintenance.csv"- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
This is working when we query directly from Splunk Search..
| stats count as field1 | eval field1="dallvcflwb110u,yes;dallvcflwb120u,yes" | eval field1=split(field1,";") | mvexpand field1 | rex field=field1 "(?<host>.*),(?<mode>.*)" | table host mode | outputlookup atlassian_maintenance.csv
But when we try hitting using curl and its failing .
curl -k -u admin:Vzadmin@12 https://dallpsplsh01sp.tpd-soe.net:8089/servicesNS/admin/SRE/search/jobs/export -d search="| stats count as field1 | eval field1="dallvcflwb110u,yes;dallvcflwb120u,yes" | eval field1=split(field1,";") | mvexpand field1 | rex field=field1 "(?<host>.*),(?<mode>.*)" | table host mode | outputlookup atlassian_maintenance.csv"
-bash: syntax error near unexpected token `?'
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi
please don't add your admin user + it's pass to any posts. Or actually write those on cmd as those are stored into history files and/or are seen on process list! Much better way is to read those into variable and then use that on queries. You could do it like
read USERPASS
admin:<your pass here>
^D
curl -ku $USERPASS .....
Also don't add your real node name into examples!
As you are in linux/*nix you could replace those outer " with ' and then it should work. Then you are not needs \" inside your SPL.
curl -ku $USERPASS https://<your splunk SH>:<mgmt port>/servicesNS/admin/SRE/search/jobs/export -d search='| stats count as field1 | eval field1="dallvcflwb110u,yes;dallvcflwb120u,yes" | eval field1=split(field1,";") | mvexpand field1 | rex field=field1 "(?<host>.*),(?<mode>.*)" | table host mode | outputlookup atlassian_maintenance.csv'In windows this didn't work ;-(
r. Ismo
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi,
can you please remove the "\" and give a try


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Meet Splunk Observability Studio: AI-Assisted OpenTelemetry Instrumentation Without ...
Federated Search for Cisco Security and Analytics Logging (SAL) is now GA on Splunk ...
Your Path to AgenticOps: AI Experiences for Every Splunk Practitioner
