
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Monitor input error
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi guys, I´ve been trying to add data on my HF and when I get to submit my input I receive this error:
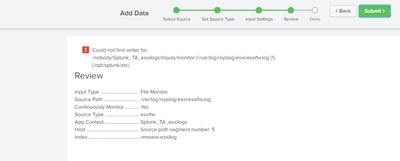
I do not know what "could not find writer for: /nobody/..." means...
Could you please help me figure it out?
Thanks in advance.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

I don't have a good idea right now. 😕
The splunk user can read the file being monitored, right?
Karma and/or Solution tagging appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @franciscof ,
You should find details in the splunkd.log
Try searching for esxifw.log, or maybe "nobody" around the time you tried to create the monitor.
Hope it helps.
BR
Ralph
Karma and/or Solution tagging appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi, this is what I see when I check on the logs from the splunkd.log
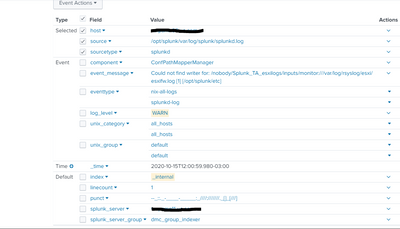
Still think this is a little unclear. What do you think?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I don't have a good idea right now. 😕
The splunk user can read the file being monitored, right?
Karma and/or Solution tagging appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
That was the issue, root had permissions on the directory, thanks for you help

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Your Path to AgenticOps: AI Experiences for Every Splunk Practitioner
The Data Connection - October 2026
Beyond the Acceleration Zone: Maximizing Your Success with Splunk Customer Experience ...
