
Turn on suggestions
Auto-suggest helps you quickly narrow down your search results by suggesting possible matches as you type.
Getting Data In
×
Join the Conversation
Without signing in, you're just watching from the sidelines. Sign in or Register to connect, share, and be part of the Splunk Community.
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: How to create dump command and put datetime?
Options
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How to create dump command and put datetime?

khyoung7410
Communicator
04-03-2018
08:26 AM
Hi
Ask about basefilename in dump command.
I would like to create a file by date with search results and I would like to put the time in basefilename as in the month and date.
What should I do?
My Search is:
 index=_audit
    | eval date=strftime(_time,"%F %T")
    | eval _dstpath=strftime(_time, "%Y%m/%d")
    | dump basefilename=splunk format=csv fields="date, user, action, info, index, sourcetype"
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
s2_splunk

Splunk Employee
04-03-2018
10:38 AM
The only thing I can think of is to create a macro, since the dump command does not accept variables directly.
Example:
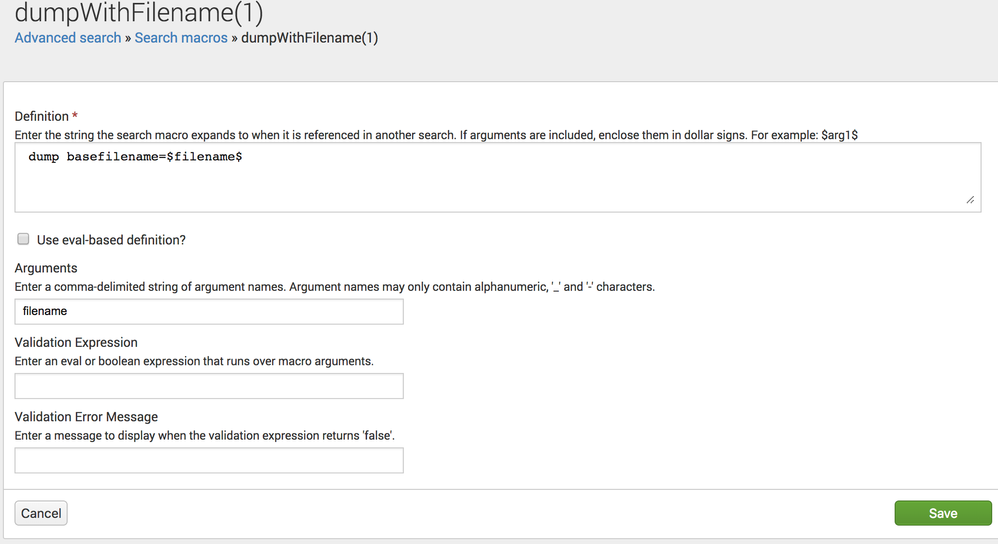
You can then do something like this:
<yoursearch> | eval myFileName="DumpFile_".strftime(now(),"%Y%m%d") | `dumpWithFilename(myFileName)`
Adjust your macro to include other parameters as needed.


Got questions? Get answers!
Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Meet up IRL or virtually!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Get Updates on the Splunk Community!
Persistent Queue at TcpOut — One of Splunk's Most Practical Features
Splunk introduced persistent queueing at the tcpout layer as one of the most practical resilience features in ...
Build resilience for the agentic era: Join us at Splunk Go San Jose
AI is changing how organizations build, operate, and secure digital services. As teams adopt AI agents and ...
Manage Edge Processor pipelines end to end with APIs
This guide uses the Data Management APIs to create an Edge Processor, onboard one instance, deploy a pipeline ...
