
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: How do I enable CORS in Splunk Enterprise ?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How do I enable CORS in Splunk Enterprise ?
I was trying to build application outside the Splunk web interface using Splunk REST APIs and Angular 6 I Got**CORS rejection error
REST API ( I used 😞 https://localhost:8089/services/auth/login
result:
*angular Code : *

  login(data) {
    const body = new URLSearchParams();
    body.set('username', data.username);
    body.set('password', data.password);
    body.set('output_mode', 'json');
    const options = {
      headers: new HttpHeaders().set('Content-Type', 'application/x-www-form-urlencoded')
  };
  console.log(body.toString());

      this.http.post('https://localhost:8089/services/auth/login', body.toString(), options).subscribe(
        (resData) => {
          console.log(resData);
        },
        (err) => {
          console.log(err);
        }
      );
    console.log(data);
    }
but it is working fine with Post man
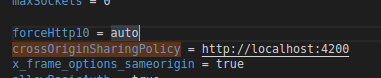
Then I tried Changing server.conf
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
If you have admin access to the Splunk server that will receive the requests there is a setting for this in server.conf.
[httpServer]
crossOriginSharingPolicy =
If the intent here is to build an application that will connect to any Splunk instance with a username and password then it is a matter of following the CORS protocol and using an API container.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


@Nagarajv
Have you tried to connect Splunk using SplunkJavascript SDK?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
ya @kamlesh_vaghela , i tried with splunk-sdk(JS) in node Js and it is working good.
but now i'm using ReST API's of Splunk and i'm getting CORSS rejection Error




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Supercharging Windows Security Detection Performance: Introducing Hybrid Field ...
Enriching Signals with the OTel Lookup Processor
Meet the .conf26 AI Agent Buildathon Winners
