
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: Forwarding and receiving - Error occurred atte...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi guys,
I configured my all-in-one Splunk instance to forward data to another search head by using an tcpout:9997 at outputs.conf. Then I removed the config file manually from Ubuntu command line.
However, I found data from my all-in-one Splunk box still forwarding to the other SH after reboot.
So I checked Forwarding and receiving setting from Splunk Web. I found the previous setting still there. Please see the attached screenshot for details.
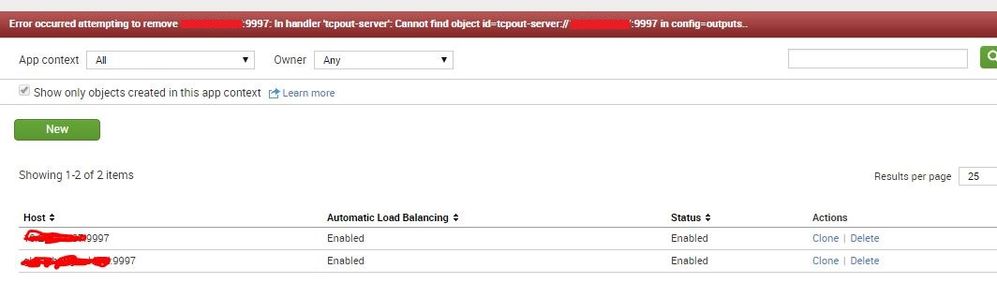
Is there a way to remove those two forward data configurations from either Splunk Web or CMD?
Could any one please help?
Cheers,
Vincent

- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi everyone,
I used btool find a configuration in one of my apps has a tcpout setup at outputs.conf.
So I removed the configuration and restart Splunk. Issue is now resolved. 🙂
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi everyone,
I used btool find a configuration in one of my apps has a tcpout setup at outputs.conf.
So I removed the configuration and restart Splunk. Issue is now resolved. 🙂
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

What was done to fix this issue? Experiencing the same thing in our environment
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi robinsonk,
I assume your Splunk is in a Linux environment as well?
You can use btool to find all configurations at outputs.conf.
Something like ./splunk cmd btool outputs list --debug | grep tcpout
Find the configuration you don't want. And manually delete the configuration from outputs.conf...
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
no we are Windows environment.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi Windows can use btool as well. It is basically the same. Just remove ./ at the beginner of the cmd.
Check here for more information:
http://docs.splunk.com/Documentation/Splunk/6.4.1/Troubleshooting/Usebtooltotroubleshootconfiguratio...

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Splunk Add-on for Microsoft Windows 11.0.3: Parse Once, Search Faster
What's New in Splunk Enterprise Security 8.8 and Beyond
A Four-Part Event Series: State of Observability - Where AI Meets Performance
