
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Dashboards & Visualizations
- :
- Re: Time range picker preview doesn't work on Hunk
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

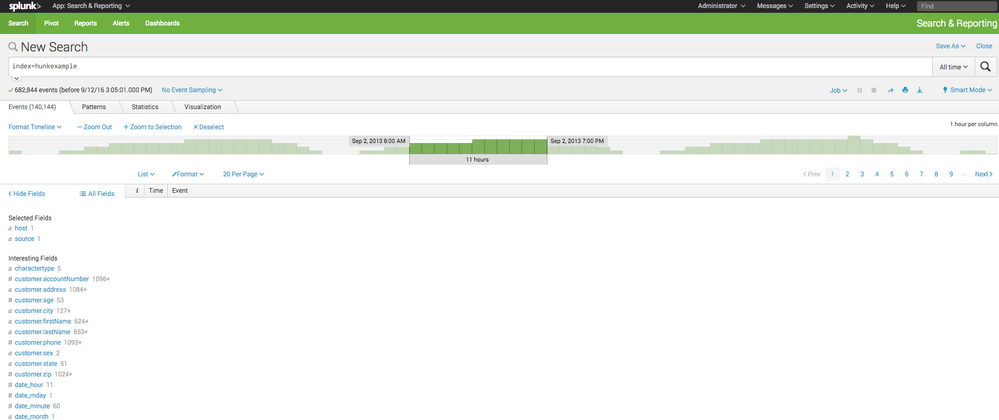
Issue = Time range picker preview doesn't work on Hunk
To reproduce:
0 = Setup Demo Hunk workload as per: http://docs.splunk.com/Documentation/Hunk/6.4.3/Hunktutorial/Tutorialoverview
1 = Run a search (e.g. index=hunkexample)
2 = Select a timeslice from the timeline.
3 = Observe that no events are returned (bottom right panel is blank).
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Answer = The time range preview picker is not expected to work on Hunk.
Cause = This is because Hunk/Hadoop cannot guarantee time ordered results (because of the way hadoop returns it's results).
Related Bugs to this:
ERP-1938 = Clarify Behaviour.
ERP-1972 = Document behaviour.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Answer = The time range preview picker is not expected to work on Hunk.
Cause = This is because Hunk/Hadoop cannot guarantee time ordered results (because of the way hadoop returns it's results).
Related Bugs to this:
ERP-1938 = Clarify Behaviour.
ERP-1972 = Document behaviour.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Please note though that if you select a range on the time range picker and double click it, Hunk will launch a new query using that time range.


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
