
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Dashboards & Visualizations
- :
- Between dates condition showing error?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Between dates condition showing error?

Hello everyone,
I am passing the dates as token but it shows the error in both the condition.
Cond1: | where (Date>="$date_start$" AND Date<="$date_end$")
Cond2: | where (Date>="2022-06-01" AND Date<="2022-06-02")
Please help
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @Neel88,
to compare dates, you have to transform them in epochtime using the strptime function, you cannot compare dates in text format.
The only apparent exception is _time, but it's only apparence because it's already in epochtime.
something like this:
<your_search>
| eval date_start=strptime($date_start$,"%Y-%m-%d"), date_end=strptime($date_end$,"%Y-%m-%d"), Date=strptime(date,"%Y-%m-%d")
| where Date>=date_start AND Date<=date_end
| ...
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
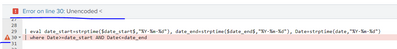
Hi @Neel88,
this is a different problem:
in the simple xml dashboards you cannout use "<" or ">" but you have to use: "<" and ">"
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thank you for your response.
| where (Date = ">","$date_start$") AND (Date = "<","$date_end$")
I am very new with this tool. I am not getting result.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @Neel88,
I used quotes to delimit the strings, use them without quotes:
<your_search>
| eval date_start=strptime($date_start$,"%Y-%m-%d"), date_end=strptime($date_end$,"%Y-%m-%d"), Date=strptime(date,"%Y-%m-%d")
| where Date>=date_start AND Date<=date_end
| ...Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thank you so much!! Its working fine 🙂

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Persistent Queue at TcpOut — One of Splunk's Most Practical Features
Catalog Is Now Generally Available on Splunk Cloud Platform
Your Path to AgenticOps: AI Experiences for Every Splunk Practitioner
