
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Other Using Splunk
- :
- Alerting
- :
- Re: timechart, timewrap output alert
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi Team,
I am looking for the help to get an alert trigger if the latest result of timechart command is 0.
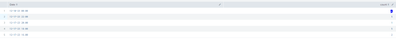
Suppose i am running a search for last 8hrs with span=2hrs. so, if the result is something like below should raise an alert.
12-18-23 00:00 ---> is "0"
and also it should is display if there is "0" events in last 8hrs. as i am getting nothing, if no events during that time.
Thank you,
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @cbiraris,
adapt this sample to you use case:
| makeresults | eval _time=strptime("2023-12-18 02:01:01","%Y-%m-%d %H:%M:%S")
| append [ | makeresults | eval _time=strptime("2023-12-18 04:01:01","%Y-%m-%d %H:%M:%S") ]
| append [ | makeresults | eval _time=strptime("2023-12-18 06:01:01","%Y-%m-%d %H:%M:%S") ]
| timechart count span=1h
| eval col=strftime(_time,"%Y-%m-%d %H:%M:%S")." - ".count
| stats values(col) AS col latest(count) AS latest
| where latest=0
it shuld be something similar to this:
<your_search>
| timechart count span=1h
| eval col=strftime(_time,"%Y-%m-%d %H:%M:%S")." - ".count
| stats values(col) AS col latest(count) AS latest
| where latest=0
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @cbiraris,
you could simplify your alert running it every two hours using a simple search:
index=your_index earliest=-2h@h latest=@hthat fires if you haven't results.
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
@gcusello Thank you for response
I also want result of previous 8hrs with 2hrs interval to be displayed in alert result.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @cbiraris,
adapt this sample to you use case:
| makeresults | eval _time=strptime("2023-12-18 02:01:01","%Y-%m-%d %H:%M:%S")
| append [ | makeresults | eval _time=strptime("2023-12-18 04:01:01","%Y-%m-%d %H:%M:%S") ]
| append [ | makeresults | eval _time=strptime("2023-12-18 06:01:01","%Y-%m-%d %H:%M:%S") ]
| timechart count span=1h
| eval col=strftime(_time,"%Y-%m-%d %H:%M:%S")." - ".count
| stats values(col) AS col latest(count) AS latest
| where latest=0
it shuld be something similar to this:
<your_search>
| timechart count span=1h
| eval col=strftime(_time,"%Y-%m-%d %H:%M:%S")." - ".count
| stats values(col) AS col latest(count) AS latest
| where latest=0
Ciao.
Giuseppe

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Splunk Add-on for Microsoft Windows 11.0.3: Parse Once, Search Faster
What's New in Splunk Enterprise Security 8.8 and Beyond
A Four-Part Event Series: State of Observability - Where AI Meets Performance
