
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Other Using Splunk
- :
- Alerting
- :
- Native Splunk Password Expiry Alert - Is it not wo...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Native Splunk Password Expiry Alert - Is it not working for anyone?
I have setup the Splunk native password policy on my company's implementation but it seems like the password expiration alert does not work as expected. Today I have many users complaining that their password has expired but did not receive, or notice any warning.
I was assuming that the 15 day alerts would be a "highlighted bar" at the top of the splunk page (fine for daily users) but for occasional users I was expecting an email. Reading over the docs I can only find information on how to set this but not any detail on what it actually does.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

The alert is displayed when a user login (image above), you have to specify some parameters in the authentication.conf (https://docs.splunk.com/Documentation/Splunk/8.0.3/Admin/Authenticationconf), to do so : declare the stanza splunk_auth and modify the following keys :
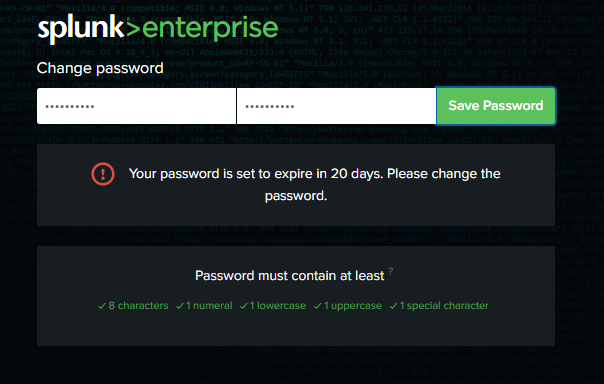
[splunk_auth]
minPasswordLength = 8
minPasswordUppercase = 1
minPasswordLowercase = 1
minPasswordDigit = 1
minPasswordSpecial = 1
expirePasswordDays = 20
expireAlertDays = 42
expireUserAccounts = True
forceWeakPasswordChange = True
lockoutUsers = True
lockoutMins = 30
lockoutAttempts = 3
enablePasswordHistory = True
passwordHistoryCount = 5


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
