
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- checkpoint Log R80.10 with log forwarder to Splunk...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
checkpoint Log R80.10 with log forwarder to Splunk (win) field extraction
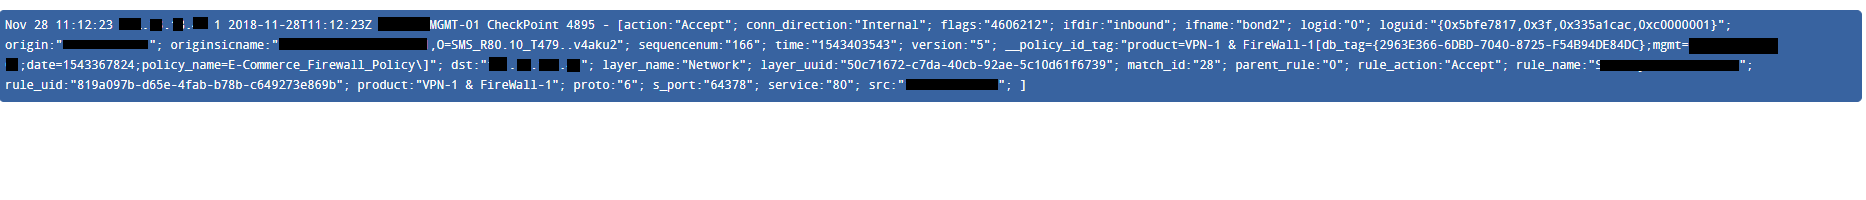
Hi - We're on R80.10 and the logs are coming through fine into a separate index.
I've installed the Check Point App for Splunk and set the source Type to cp_log
However none of the fields are properly searchable?
Do I have to use the Extract Fields process? When I tried this with a ; delimiter I get the error below, is this something I'm doing wrong? thanks for any help!
Error in 'rex' command: regex="(?ms)^(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))(?:\x3b)?(?P(?:"(?:[^\"]|.)"|(?:(?:(?!(?:\x3b)|\|").)|(?:.))))" has exceeded the configured depth_limit, consider raising the value in limits.conf.



Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Data Management Digest – September 2026
Federated Search for CloudWatch Unified Data Store Is Generally Available
Announcing Modern Navigation: A New Era of Splunk User Experience
