
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: eval case not evaluating fields
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi,
i have a field with the models, like below, and with this info i want to define a new field like brand.
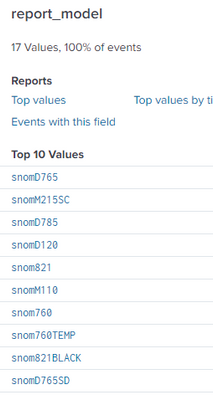
i tried different approaches but can't get brand field populated, below a test search with different case, none works but where clause works well.
index=core_ct_report_*
| where (report_model = "cfgHT802")
| eval brand=case(report_model=cfgHT802, grandstream)
| eval brand2=case(like(report_model, cfgHT802), grandstream)
| eval brand3=case(like(report_model, "cfg%"), grandstream)
| table report_model brand brand2 brand3

what is wrong?
What i need is something like this,
| eval brand3=case(like(report_model, "cfg%"), grandstream, ...)
Thanks,
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


What is grandstream? If it is a field with content, then at least brand3 should have worked. If it is supposed to be a string, then it needs to be quoted (as do the other strings
| eval brand=case(report_model="cfgHT802", "grandstream")
| eval brand2=case(like(report_model, "cfgHT802"), "grandstream")
| eval brand3=case(like(report_model, "cfg%"), "grandstream")- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thanks both for the inputs @ITWhisperer @yuanliu
the problem is the missing double quotes on the true condition like @ITWhisperer said.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
What is grandstream? If it is a field with content, then at least brand3 should have worked. If it is supposed to be a string, then it needs to be quoted (as do the other strings
| eval brand=case(report_model="cfgHT802", "grandstream")
| eval brand2=case(like(report_model, "cfgHT802"), "grandstream")
| eval brand3=case(like(report_model, "cfg%"), "grandstream")- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
First, note that screenshots are very unfavorable for volunteers. Please use text for illustration wherever possible.
Secondly, SPL interprets bare strings on the right-hand side (evaluation expressions) as field names. To match strings, you need to quote them properly.
index=core_ct_report_*
| where (report_model = "cfgHT802")
| eval brand=case(report_model=="cfgHT802", grandstream)
| eval brand2=case(like(report_model, "cfgHT802"), grandstream)
| eval brand3=case(like(report_model, "cfg%"), grandstream)
| table report_model brand brand2 brand3

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Meet Splunk Observability Studio: AI-Assisted OpenTelemetry Instrumentation Without ...
Federated Search for Cisco Security and Analytics Logging (SAL) is now GA on Splunk ...
Your Path to AgenticOps: AI Experiences for Every Splunk Practitioner
