
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: TIme Conversion
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi ,
how to change the below raw time field to yyyy-mm-dd hh:mm:ss
2020-09-09T18:21:12.2685607Z
am using the below query and didnt get any result
eval time = strftime(activityDateTime,"%Y-%m-%d %H:%M:%S")
Can someone please help
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

check updated answer.
If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
strftime is used to convert unix timestamp to human readable format.
you should use strptime to convert time which is already in human readable format if you need to format it.
| makeresults | eval activityDateTime="2020-09-09T18:21:12.2685607Z"
| eval time = strftime(strptime(activityDateTime,"%Y-%m-%dT%H:%M:%S"),"%Y-%m-%d %H:%M:%S")If this helps, give a like below.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

still in the old format, and time column is still blank
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

What do you mean by raw time field? What fields do you have? Do you get anything in the time field you created?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
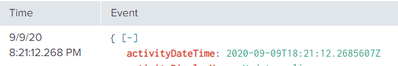
No i didnt get anything.
raw time field - time format which i get in the event
activityDateTIme
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Looks like you need to parse the activityDateTime with strptime and then format that with strftime
eval time = strptime(strptime(activityDateTime, "%Y-%m-%dT%H:%M:%S.%Q"),"%Y-%m-%d %H:%M:%S")Or you could just parse the activityDateTime string into an epoch time and the use fieldformat on the time field for display purposes

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Manage Edge Processor pipelines end to end with APIs
Splunk Brings Proof of Control to Digital Asset Transfers
Manage Ingest Processor pipelines end to end with APIs
