
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Unable to get multiple legends on x axis
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi Team,
Following is my data:
| SS | TT | DT | DA | LT | LA | TO | TA |
| a | xxx | 4 | 3 | 2 | 3 | 7 | 6 |
| a | yyy | 2 | 2 | 2 | 3 | 4 | 5 |
| b | xxx | 1 | 1 | 1 | 1 | 3 | 3 |
| b | yyy | 1 | 1 | 1 | 1 | 1 | 1 |
following is the graph i can populate in excel

Following is the graph I was able to populate in splunk
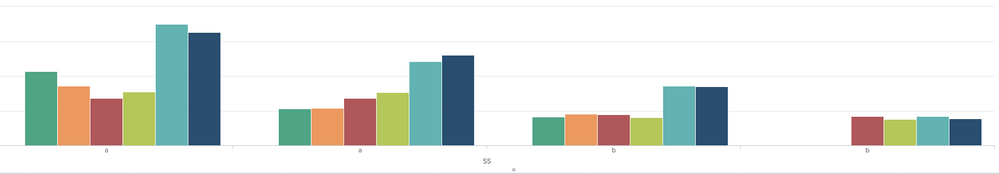
My problem is I can "SS" written in the Splunk graph, also I can see "a" "b" written in the graph....but along from these i also need "xxx" "yyy" to appear as legend under all 4 graphs.
how can we do that?
MY QUERY FOR DATA
|stats sum(* ) by SS,TT
|foreach sum* [eval <<FIELD>> = round(('<<FIELD>>' * 1000),2) ]
|rename sum(*) as *
|stats values(*) by SS,TT
|rename values(*) as *
|table SS,TT,DT,DA,LT,LA,TO,TA
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Simple answer is that it is not how standard charts work.
You could merge SS and TT
| eval SS=SS.":".TT
| fields - TT- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thanks a lot !! You saved me so much of Energy !! 🙂
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Simple answer is that it is not how standard charts work.
You could merge SS and TT
| eval SS=SS.":".TT
| fields - TT

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Vibe-coding, AI, and Splunkcraft: Highlights from the .conf26 Builder Bar
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
