
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- How create line chart using Time and Date
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How create line chart using Time and Date

Hi Guys,
I need your help.
I have this structured log:
SERVICE,END_TIME,DATA,TIME
Job_Name,10/12/2018 07:14,10/12/2018,07:14
Job_Name,12/12/2018 07:14,12/12/2018,07:14
Job_Name,13/12/2018 09:04,13/12/2018,09:04
Job_Name,14/12/2018 11:11,14/12/2018,11:11
I need to create this graph where there is Time (Hour) in Y-axis and Date (Days) in X-axis:

Which is the correct way?
Thanks in advance for the help.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

As far as I am aware, you can't make the Y axis in Splunk be non-numeric. It will split the values into different lines for each timestamp you have there instead of a single line.
Documentation: https://docs.splunk.com/Documentation/Splunk/7.2.5/Viz/LineAreaCharts#Data_formatting
| makeresults count=1
| eval data="Job_Name,10/12/2018 07:14,10/12/2018,07:14
Job_Name,12/12/2018 07:14,12/12/2018,07:14
Job_Name,13/12/2018 09:04,13/12/2018,09:04
Job_Name,14/12/2018 11:11,14/12/2018,11:11"
| fields - _time
| rex field=data max_match=0 "(?<data>[^\n\e]+)"
| eval data=trim(data)
| mvexpand data
| rex field=data "(?<SERVICE>[^\,]+),(?<END_TIME>[^\,]+),(?<DATA>[^\,]+),(?<TIME>[^\e]+)"
| eval DATA=strftime(strptime(DATA, "%d/%m/%Y"), "%d-%b-%y")
| eval TIME=strftime(strptime(TIME, "%H:%M"), "%H:%M:%S")
| eval count=1
| xyseries DATA TIME count
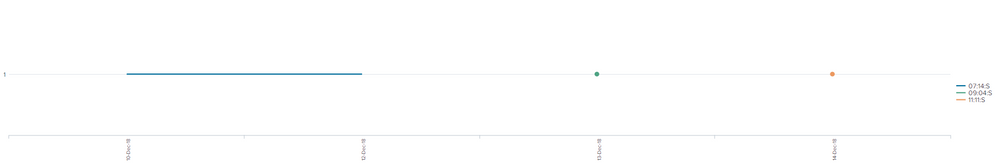
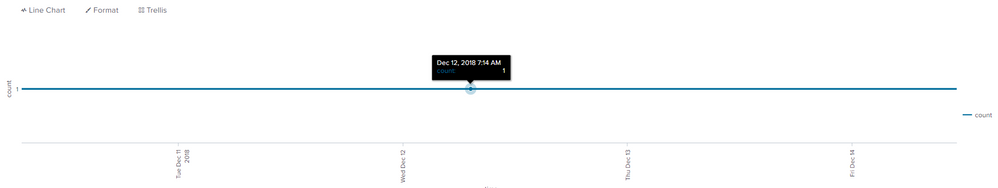
A timechart would probably be more beneficial, but it won't have that timestamped Y axis and you would need to hover over the visualization to see the minute:
| makeresults count=1
| eval data="Job_Name,10/12/2018 07:14,10/12/2018,07:14
Job_Name,12/12/2018 07:14,12/12/2018,07:14
Job_Name,13/12/2018 09:04,13/12/2018,09:04
Job_Name,14/12/2018 11:11,14/12/2018,11:11"
| fields - _time
| rex field=data max_match=0 "(?<data>[^\n\e]+)"
| eval data=trim(data)
| mvexpand data
| rex field=data "(?<SERVICE>[^\,]+),(?<END_TIME>[^\,]+),(?<DATA>[^\,]+),(?<TIME>[^\e]+)"
| eval _time=strptime(DATA.TIME, "%d/%m/%Y%H:%M")
| timechart span=1m count
| search count>0


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Make Your Machine Data AI-Ready in Splunk
Splunk Asynchronous Forwarding Explained
How to Monitor AI Agents with Splunk Agent Observability
