
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Re: Help in field extraction
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hello,
Sorry for a newbie question, I have the following event thats generated
{
@timestamp: 2021-06-03T17:39:34.720+00:00
@version: 1
correlation: test12345
message:{"code":200,"data":{"status":"status1234"}}
}
What query should I use to extract status, my requirement is when I execute my query it should come in a tabular form as follows
status status1234
Thanks in advance.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Can you please try this?
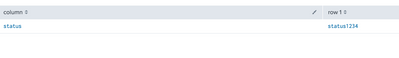
YOUR_SEARCH |spath message.data.status | rename message.data.* as * | table status | transpose
My Sample Search :
| makeresults | eval _raw="{\"@timestamp\": \"2021-06-03T17:39:34.720+00:00\",\"@version\": \"1\", \"correlation\": \"test12345\",\"message\":{\"code\":200,\"data\":{\"status\":\"status1234\"}}}"|spath message.data.status | rename message.data.* as * | table status | transpose
Thanks
KV
▄︻̷̿┻̿═━一
If any of my reply helps you to solve the problem Or gain knowledge, an upvote would be appreciated.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Thanks, is it possible to give me the sample spath command that I can use? Tried searching but not getting a proper answer.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Can you please try this?
YOUR_SEARCH |spath message.data.status | rename message.data.* as * | table status | transpose
My Sample Search :
| makeresults | eval _raw="{\"@timestamp\": \"2021-06-03T17:39:34.720+00:00\",\"@version\": \"1\", \"correlation\": \"test12345\",\"message\":{\"code\":200,\"data\":{\"status\":\"status1234\"}}}"|spath message.data.status | rename message.data.* as * | table status | transpose
Thanks
KV
▄︻̷̿┻̿═━一
If any of my reply helps you to solve the problem Or gain knowledge, an upvote would be appreciated.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Meet the .conf26 AI Agent Buildathon Winners
Trusted Autonomy in the SOC: A Maturity Journey
Supercharging Windows Security Detection Performance: Introducing Hybrid Field ...
