
Join the Conversation
- Find Answers
- :
- Splunk Products
- :
- Splunk Enterprise
- :
- Sort a date in string format.
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Sort a date in string format.

hi
My requirement is to create a graph for incident vs time and sort them according to my field opened_at.
But while sorting what i observe is it sorts only by one thing,either year or month or date.
So now i have dates as Mar 2015,Feb,2018,Feb 2015,March 2016.
I want the sorted form as Mar 2015,Feb,2015,March 2016, Feb 2018.
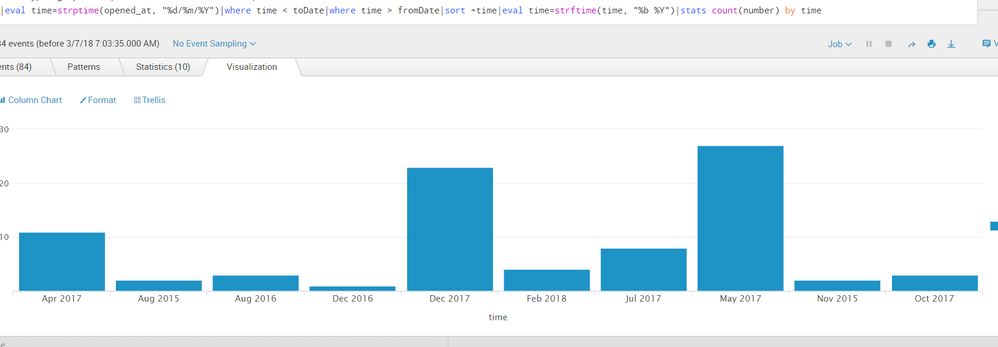
Thank you
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Move your time formatting after the stats command
Replace
... | eval time=strftime(time,"%b %Y") | stats count(number) by time
With
... | stats count(number) by time | eval time=strftime(time,"%b %Y")
The time was in epoch format, so it'll sort correctly. You can just format it to user friendly after stats so sorting is maintained. With strftime invoke earlier, the timestamp is converted to string and sorting is done alphabetically not chronologically.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
hey somesoni2
Thanks for replying my query.
I had already tried the solution which you gave ... | stats count(number) by time | eval time=strftime(time,"%b %Y")
issue with this is the incidents gets grouped by day not month.
Like earlier all the incidents for a given month were in same bar but now there are individual bars for every day.
I need to group it by months.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Kubernetes Alerts That Work Out of the Box with AutoDetect detectors in Splunk ...
Observability at Your Fingertips Directly From Splunk Platform—for Free
Accelerate Splunk App Development with AI
