
Join the Conversation
- Find Answers
- :
- Splunk Products
- :
- Splunk Enterprise
- :
- How do I make a POST request to the HTTP Event col...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How do I make a POST request to the HTTP Event collector using Splunk Light?

I set up an new Splunk Light account to test out the functionality of Splunk and would like to send data using the HTTP Event Collector.
According to the docs (http://dev.splunk.com/view/event-collector/SP-CAAAE7F), I am supposed to enable the HTTP Event Collector, which I have done:
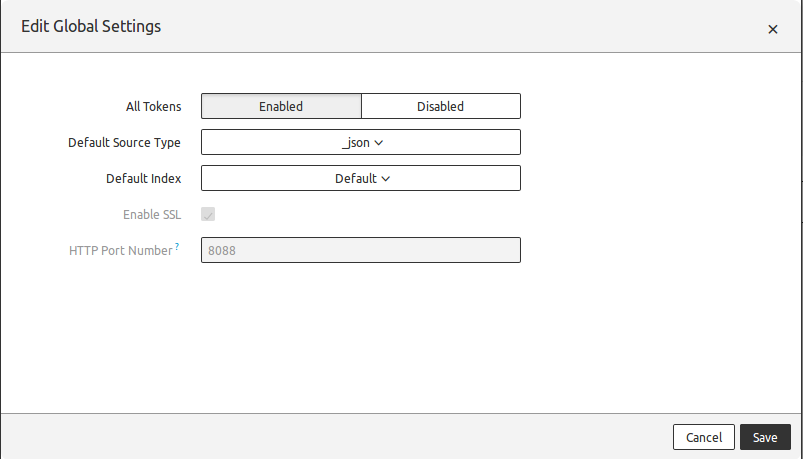
and then create a token, which I have done:
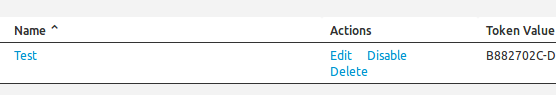
But on the review page, there is not "Host" value. I assume the host is the same host that I am using the create the tokens, something like:
https://prd-p-2lsvqbvxyzzzzz.cloud.splunk.com
So according to the docs, I should be able to post data, but for some reason it times out:
curl -k https://prd-p-2lsvqbxyzzzzz.cloud.splunk.com:8088/serivces/collector -H "Authorization: Splunk my-secret-token" -d '{"sourcetype": "curl", "event":"Hello, World!"}'

curl: (7) Failed to connect to prd-p-2lsvqbxyzzzzz.cloud.splunk.com port 8088: Connection timed out
Any idea why it is failing? Do I have everything set up correctly?
Thanks!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Because you have misspelt the endpoint in the URL ( serivces/collector) instead of ( services/collector)
This is what you have:
https://prd-p-2lsvqbxyzzzzz.cloud.splunk.com:8088/serivces/collector
This is what it should be:
https://prd-p-2lsvqbxyzzzzz.cloud.splunk.com:8088/services/collector




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
