
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Other Using Splunk
- :
- Other Usage
- :
- csv report has some lines split in multiple cells
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
csv report has some lines split in multiple cells

Hi all,
tabled results from a scheduled search are sent via email as a csv attached. Some rows could be very long so in some cases, when I open that csv file with Excel, I find some "split rows", I would expect one unique line per row but instead sometimes I have half line positioned in the second column (as in the screenshot below).
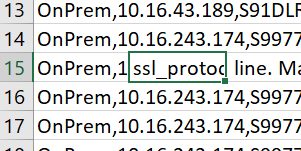
I'd like to obtain only one entire line per row, so every event only in the first column of the Excel.
The source search finds some events and tables some fields as result.
Thanks in advance for any hint.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I found out that Excel rows are splitted in multiple columns when semicolon character is used. I want to highlight that I have this problem both when I use export button on a search results and when reports send emails with csv attached.
For example, this is a screenshot of the search result:
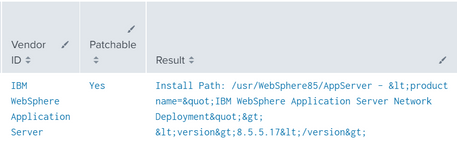
and this is how I find events for "Result" field once I export them and I open them in Excel:

with the line splitted when it encounters a semicolon.
Is there a way to change CSV delimiter for export action or other options? Do I have to set a custom sendmail.py for my app?


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
